Management and executives
“You bear responsibility. Can you properly assess risks and proposed measures?”
All matching courses →Home / Training
Online compliance training · NIS2 · DORA · CRA
Twenty-five online courses for management, information security, IT operations, product development and all employees, including three DORA courses and two courses for outsourcing officers in financial entities, four role-based data protection courses, BCM according to BSI Standard 200-4 and the new practitioner course on BSI Grundschutz++. With quizzes, a numbered certificate of attendance and evidence documents that stand up to supervisors and auditors.
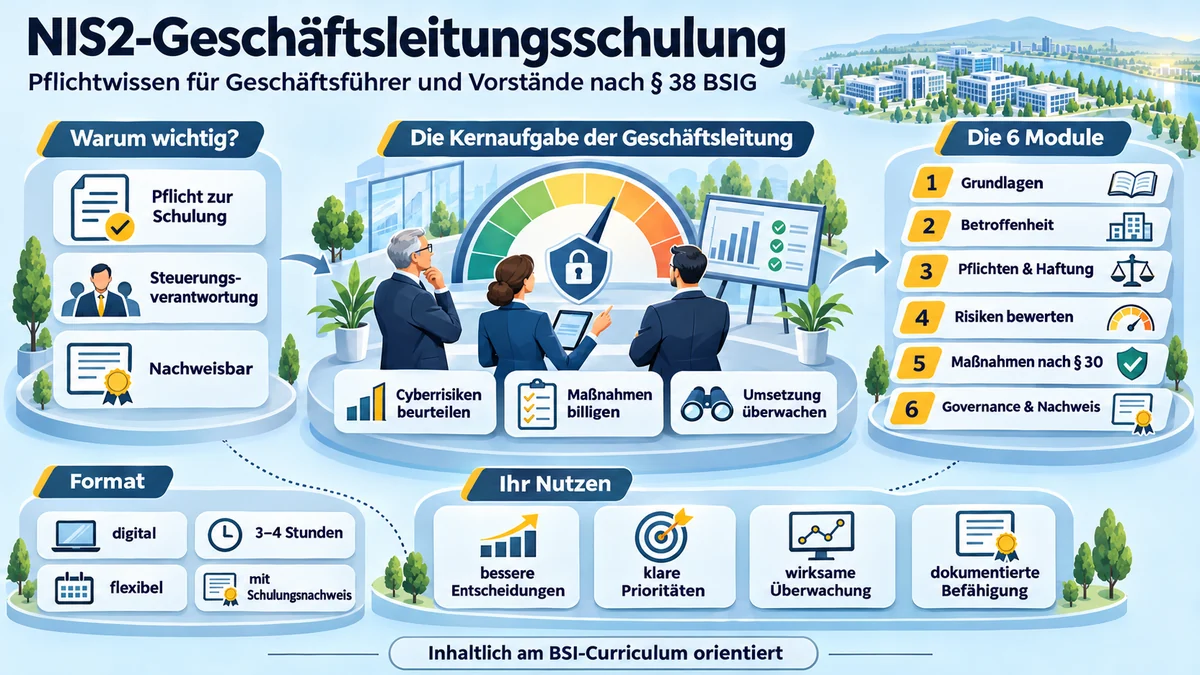
The management board training at a glance: core tasks, six modules, format and benefits.
Specialist courses
Companies need people who recognise risks, make sound decisions and can act in an emergency. Knowing the regulations or having completed a basic course is not enough. What matters is being able to apply the knowledge to your own role: Which questions do I need to ask? How do I recognise a weakness? What evidence do I need? And when do I have to step in?
Our specialist courses start where general knowledge turns into concrete responsibility. This applies to management as much as to those responsible for IT, information security, data protection, outsourcing, emergency management and internal audits.
Anyone who manages service providers must be able to assess service commitments, security evidence and dependencies. Anyone responsible for contingency planning must understand whether a recovery can actually work. Anyone who approves access rights must be able to assess the associated risks. And anyone who receives security reports needs the knowledge to question results critically and demand the right measures.
Competence also determines security and the ability to act outside these specialist roles. Employees must recognise deception attempts and handle information and AI applications consciously. Managers must set priorities, clarify responsibilities and make decisions even under time pressure. Auditors need a sound understanding to assess how meaningful evidence is and how effective measures are.
The topics therefore range from information security, data protection and AI through risk assessment, access management and service provider management to incident response, emergency management, restore tests and internal audits.
Choose courses according to your employees’ tasks and your company’s challenges. This turns training into a targeted investment in better decisions, effective controls and resilient cooperation between management, business units and IT.
Talk to us. Together we put together a training package that fits your responsibilities and your qualification needs. Request a training package →
Guide
Seven target groups, seven typical questions. Choose your role and go straight to the right course.
“You bear responsibility. Can you properly assess risks and proposed measures?”
All matching courses →“You receive reports and certificates. Can you tell from them whether your service provider meets your requirements?”
All matching courses →“Your measures are in place. How do you know whether they work in day-to-day operations and in an emergency?”
All matching courses →“The documentation exists. How do you assess implementation, effectiveness and remaining risks?”
All matching courses →“The emergency plan is written. Can the people involved act on it?”
All matching courses →“How do you turn general security advice into concrete competence to act?”
All matching courses →“How do you create transparency about software components and the related security questions?”
All matching courses →The programme at a glance
Every course ends with a verifiable certificate. You book all courses as an annual subscription in the base, NIS-2 or DORA/MaRisk package, or individual specialist courses without a subscription. To the packages and prices
Filter by target group:
Sec. 38(3) BSIG
For managing directors and executive boards, aligned with the BSI curriculum.
Sec. 30(2) no. 7 BSIG
For those leading the annual incident response exercise.
Regulation (EU) 2024/2847
For product, development and security teams at manufacturers.
NIS2 · DORA · ISO 27001
For IT governance, information security officers, auditors and IT operations, based on the ISACA guide.
Sec. 30 BSIG · Awareness
For all staff: basics, typical attacks and the right response in an emergency.
Sec. 30 BSIG · Awareness
For all staff: recognise and report phishing across all channels.
Art. 5(4) DORA
For executive and supervisory boards of financial entities: ultimate responsibility and governance.
Art. 13(6) DORA
The mandatory module for all staff: recognise, report, act securely.
Regulation (EU) 2022/2554
For risk, security, operations and internal audit: all DORA domains with gap analysis.
BSI Standard 200-4 · DER.4
For BCM officers, information security and emergency and crisis teams: the complete BCM lifecycle.
BSI Standard 300-1 · New
For CISOs, auditors and IT operations: the complete Grundschutz++ methodology from scope to the ISMS in operation.
NIST SP 800-61 · ISO/IEC 27035 · New
For IT emergency teams, first responders, IT management and crisis teams: from the first alert to lessons learned, with five playbooks and the reporting deadlines under Section 32 BSIG, GDPR and DORA.
MaRisk AT 9 · DORA · NIS-2
Legal framework, classification, steering and the officer’s role, with case studies.
MaRisk AT 9 · DORA · NIS-2
Lifecycle, contracts, registers, service provider management and audit reports in daily practice.
GDPR · BDSG
For all staff: principles, duties, reporting a data breach.
GDPR · BDSG
Responsibility, accountability, processors and liability.
GDPR · BDSG
Art. 32, privacy by design, third countries and § 202a StGB.
GDPR · BDSG
Employee data protection, personnel files and works council.
Art. 4 AI Act · New
For all employees: use generative AI safely, protect data, check results, spot fraud.
ISO/IEC 27001 · ISO 19011 · New
For ISOs, internal auditors and internal audit functions: plan, audit, assess evidence and write findings that hold up.
ISO/IEC 27005 · BSI 200-3 · New
For ISOs, risk owners, IT management and business units: formulate scenarios, assess with scales, credit controls, get decisions made.
ISO/IEC 27001 · BSI ORP.4 · New
For IT administration, application owners and managers: request, approve, revoke and recertify access rights on a business basis.
BSI 200-4 · CON.3 · ISO 22301 · New
For IT operations, backup, contingency planning and business units: plan tests, run them safely, measure honestly and obtain business sign-off.
ISO/IEC 27001 · ISO/IEC 27036 · New
For service providers: answer security questionnaires with evidence from a security profile and release answers in a controlled way.
ISO/IEC 27001 · BSI OPS.1.1.3 · New
For IT operations, security and system owners: verify findings, prioritise by situation, treat them and close them after checking.
Training as a Service
One contract, one portal, one record. From €17 per employee per year, role-based and specialist courses in the NIS-2 or DORA/MaRisk package.
Vercora training portal · included in every package
All 25 courses run on the Vercora training portal: booked, managed and evidenced centrally. You can see at any time who was trained on what and when, and when the next refresher is due. In your own branding on request.
You book seats per course. Your responsible staff receive access to the training portal.
Each person receives a personal invitation link, without a password and usable on any device.
Lessons with knowledge checks, passed from 75%. Progress is saved.
Numbered certificate with online authenticity check. The portal shows when refresher training is due.
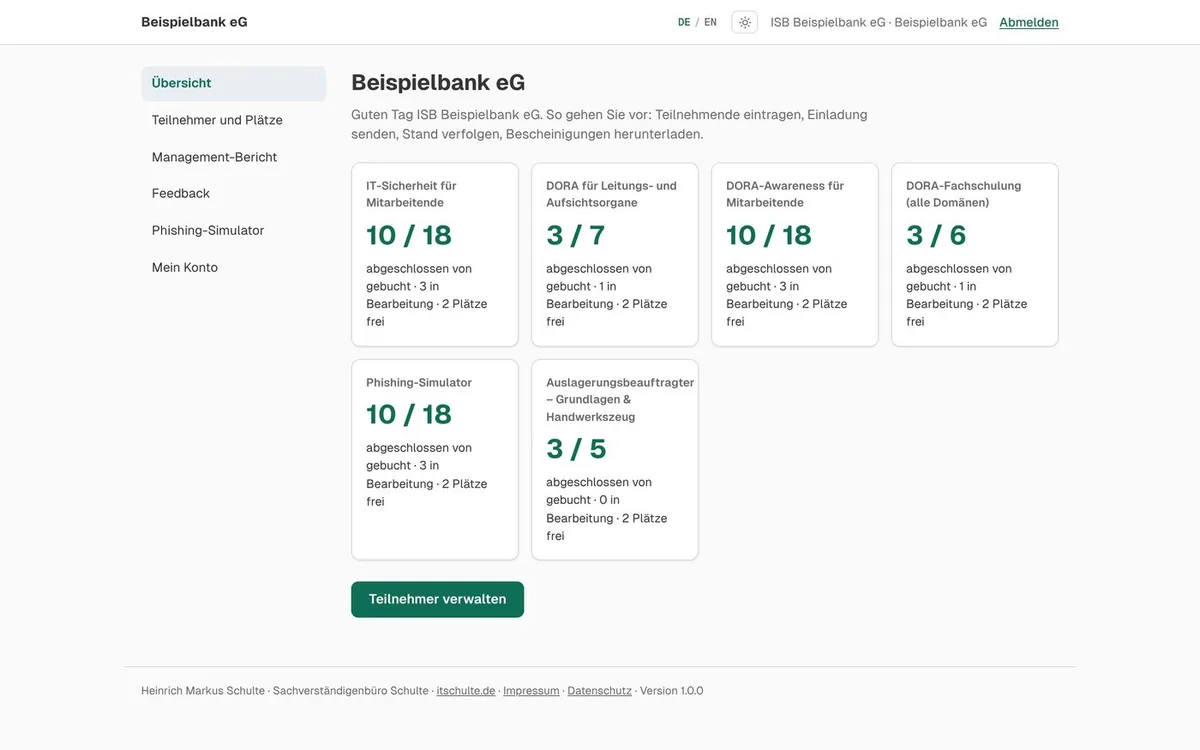
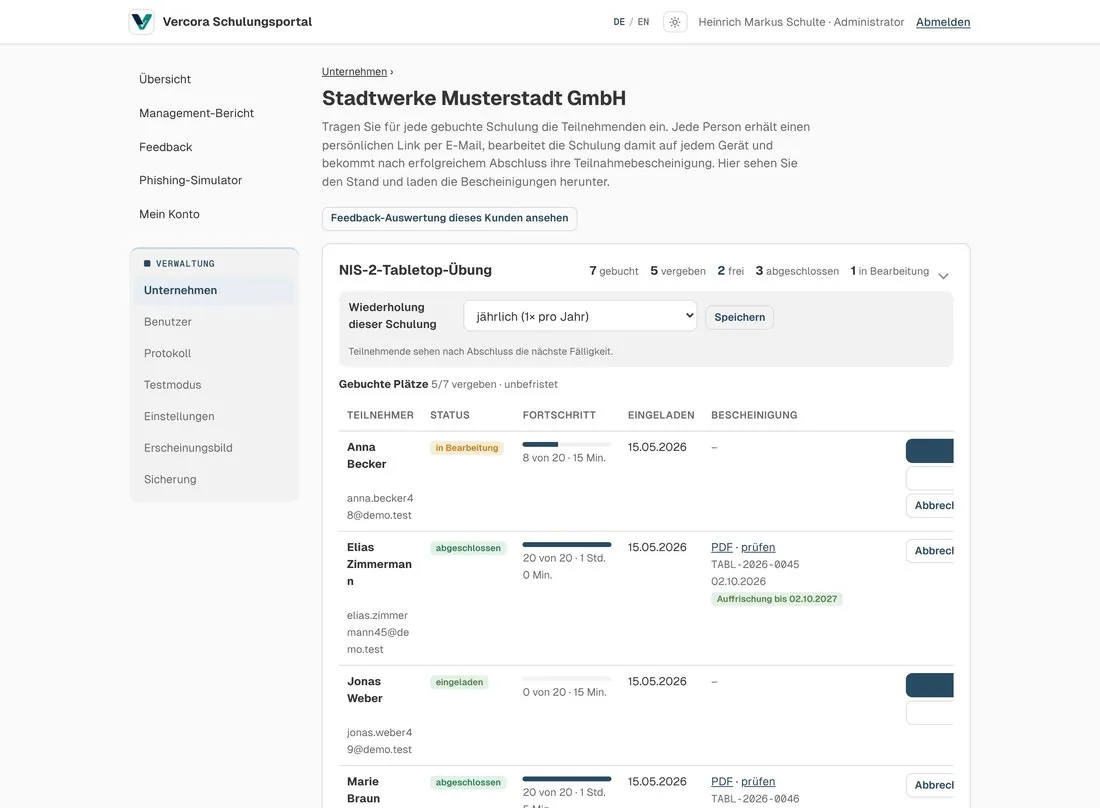
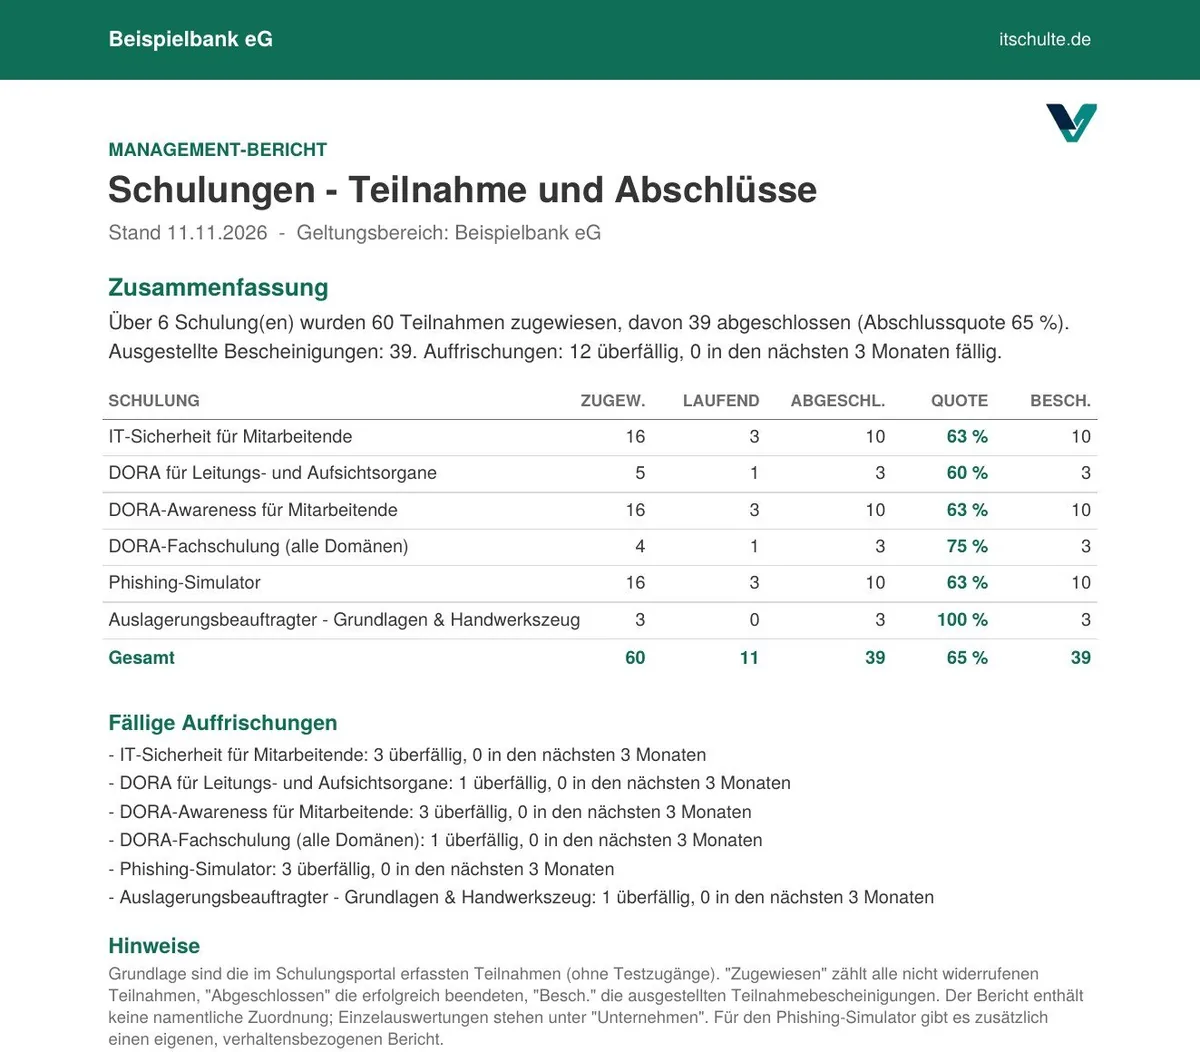

Invite participants, track progress, set the refresher interval, retrieve report and participant list
Personal link without password, on all devices, progress is saved, certificate by email
Online authenticity check of every certificate, hash-chain log, lists as PDF and CSV
Auditor’s view
“The first question in every audit is: who was trained on what, and when? The portal answers it with one click.”
Heinrich Markus Schulte · IT auditor and expert witness
Brochure as PDF (6 pages, German, 720 KB)
An auditor's view, not standard e-learning
Heinrich Markus Schulte, IT auditor and expert for information security and resilience, with more than 30 years of hands-on IT experience. The courses show not only what the law says, but which information, decisions and evidence actually count in an audit.
Training as a Service · all prices net plus VAT
One contract, one invoice, all mandatory training. Your annual price has two parts: a price per employee for everything all staff need, and a base fee for the role-based and specialist courses in your package.
Annual price = Package base fee + Employees × price per person
For every company
from €17 per employee per year
| up to 100 employees | €29 |
|---|---|
| 101 to 500 | €23 |
| 501 or more | €17 |
At least 20 employees, i.e. from €580 per year.
Request base packageRecommended for NIS-2
from €1,490 base fee per year plus base package
| up to 100 employees | €1,490 · 5 seats |
|---|---|
| 101 to 500 | €2,490 · 10 seats |
| 501 or more | €3,990 · 20 seats |
Seats apply to the tabletop exercise, BCM and Grundschutz++.
Request NIS-2 packageFor banks and insurers
from €3,900 base fee per year plus base package
| up to 100 employees | €3,900 · 5 specialist seats |
|---|---|
| 101 to 500 | €5,900 · 10 specialist seats |
| 501 or more | €8,900 · 20 specialist seats |
Specialist seats can be freely distributed across the specialist courses.
Request DORA/MaRisk package| Add-on | Price per year |
|---|---|
| CRA: SBOM and manufacturer obligations, up to 5 people | €690 |
| Incident Response and Playbooks, per person | €499 |
| Internal ISMS audits, per person | €399 |
| Assessing and treating risks, per person | €399 |
| Access management, per person | €399 |
| Restore tests, per person | €399 |
| Security evidence, per person | €399 |
| Vulnerability management, per person | €399 |
| SIEM use cases, up to 5 people | €790 |
| Data Protection for IT Professionals and HR, up to 10 people | €490 |
| Individualised phishing scenarios | +15% on the base price |
| Additional seats and specialist seats | Single-seat price minus 30% |
| Course | Price per person |
|---|---|
| NIS2 management board training | €249 |
| DORA for Management and Supervisory Bodies | €199 |
| NIS2 tabletop exercise | €149 |
| CRA: SBOM and manufacturer obligations | €199 |
| SIEM use cases | €299 |
| Emergency Management and BCM | €499 |
| BSI Grundschutz++ Practitioner | €599 |
| Incident Response and Playbooks | €499 |
| Conducting Internal ISMS Audits in Practice | €399 |
| Assessing and Treating Information Security Risks | €399 |
| Access Management and Recertification | €399 |
| Planning and Assessing Restore Tests | €399 |
| Creating Security Evidence for Customers and Clients | €399 |
| Vulnerability Management from Finding to Closure | €399 |
| DORA Specialist Training (all domains) | €590 |
| Outsourcing Officer: Fundamentals or Practitioner | €690 each, both €1,190 |
| Data Protection for Managers | €59 |
| Data Protection for IT Professionals or HR | €99 each |
Courses for all staff are only available in the base package.
E-learning provides the knowledge; live, we answer your questions and move your topic forward. Online via video conference with Heinrich Markus Schulte, bookable for any of the 25 courses, with or without a subscription.
Clarify questions
€290 net · 60 minutes
Tackle a topic
€890 net · 3 hours
For subscribers
€1,290 net · per year
Office hours and workshops convey expertise and support implementation; they are not legal advice. Dates by arrangement.
Base package, minimum of 20 employees at €29
NIS-2 package: €1,490 base fee plus 50 × €29
DORA/MaRisk package: €3,900 base fee plus 80 × €29
All prices net plus VAT. The subscription includes all content, updates, quizzes and certificates of attendance, with an evidence list per person for internal audit and supervisors. Single seats with 12 months of access including updates. Free trial access to the BCM course, demo on request.
Your contact: Heinrich Markus Schulte
IT expert witness and IT auditor with 30 years of hands-on IT experience. Examines IT the way supervisors and statutory auditors do.
Try it free
See for yourself: try the course “Emergency management and BCM according to BSI Standard 200-4” with lessons, infographics and quizzes, exactly as your participants experience it.
Frequently asked questions
Under Sec. 38(3) BSIG, the management of important and essential entities must attend training regularly so they can assess cyber risks and risk management practices. Training the IT manager or information security officer does not replace this.
No. The management board training is aligned with the BSI curriculum for NIS2 management board training. All courses are independent offerings of Sachverständigenbüro Schulte and are not certified or approved by the BSI.
Each participant receives a personal invitation link, without a password and usable on any device. Progress is saved; a knowledge check is passed from 75%. The certificate of attendance arrives as a PDF by email, with a number and online authenticity check.
No. The tabletop training is role-based training for exercise leads under Sec. 30(2) no. 7 BSIG. It does not fulfil management's training obligation under Sec. 38(3) BSIG.
The Cyber Resilience Act has no personal training obligation. The CRA course helps manufacturers implement their obligations, such as the SBOM under Annex I Part II no. 1 and the reporting obligations under Art. 14. The certificate proves the training, not the conformity of a product.
No. The course is vendor-neutral and follows the system-independent guide “Security Use-Cases – ein Katalog” by ISACA Germany Chapter e. V. Examples of event codes and scripts refer to Windows and Linux.
No. The certificate of attendance proves the training. It is not a certification of SIEM operations and not an audit attestation. For evidencing use case coverage, the course includes reporting and evidence templates.
For all staff, no prior IT knowledge required. The course takes about 107 minutes, ends with knowledge checks and a certificate of attendance, and so supports cyber hygiene training under § 30(2) no. 7 BSIG. It does not meet the separate training obligation for management under § 38(3) BSIG; the management training covers that.
No. The exercise runs fully simulated in the browser, in an inbox just like at work. All senders, companies and links are fictitious, no real credentials are requested and nothing is actually opened or sent. Leadership receives an anonymised management report.
Under Art. 5(4) DORA, the management body must keep its knowledge up to date through regular training; the course for management and supervisory bodies covers this. For all staff, awareness and resilience training are compulsory modules under Art. 13(6); DORA Awareness covers this. Those who implement or audit DORA, such as risk, security, operations and internal audit, use the specialist training. In the DORA/MaRisk package you book all three as an annual subscription for the whole organisation.
For BCM officers, IT and information security managers and emergency and crisis teams. The course covers the complete BCM lifecycle based on BSI Standard 200-4, from the BIA pre-filter to exercises and management review, and ends with a verifiable certificate of attendance. It is included in the NIS-2 package and the DORA/MaRisk package; as a single seat it costs €499 net per person.
Yes, in two consecutive courses of about ten hours each. “Fundamentals and Toolkit” covers the legal framework, classification and steering of outsourcing under DORA, MaRisk AT 9 and NIS-2. “Practitioner” covers the lifecycle, contracts, registers, service provider management and evaluating audit reports. Both courses are included in the DORA/MaRisk package; as single seats they cost €690 net per person each, €1,190 together.
Four role-based online courses under the GDPR and BDSG: for all employees, for managers, for IT professionals and for the HR department. Each ends with a verifiable certificate of attendance. Data Protection for Employees is included in the base package, Data Protection for Managers in the NIS-2 package, IT and HR are available as an add-on.
The annual price consists of a price per employee and a base fee. The base package with IT security, phishing simulator, Data Protection for Employees and AI in Everyday Work costs €29 net per employee per year up to 100 staff, €23 up to 500 and €17 above that, with a minimum of 20 employees. The NIS-2 package adds a base fee from €1,490 per year, the DORA/MaRisk package from €3,900. A NIS-2 company with 50 employees thus pays €2,940 net per year.
Yes. The practitioner course “BSI Grundschutz++ Practitioner” teaches the approach according to BSI Standard 300-1: survey scope and protection requirements, derive the requirements package from target object categories, treat risks according to the minimum criteria and operate the ISMS in the PDCA cycle. 12 modules, 39 lessons, approx. 11 hours, with three industry case studies. Included in the NIS-2 and DORA/MaRisk packages, single seat €599 net per person.
Yes. “Vulnerability Management from Finding to Closure” shows, from the operator’s perspective and based on ISO/IEC 27001 Annex A, BSI modules OPS.1.1.3 and DER.1 and Section 30 BSIG, how to verify findings from scanners and vendor advisories, prioritise them by exposure, known exploitation (EPSS, KEV catalogue), severity, existing safeguards and business relevance, time-limit exceptions, escalate deadlines and close only after a verification check. The course deliberately does not give universal remediation deadlines; you learn to set your own deadlines with a justification. Case workshop with five reports and seven templates. 6 modules, 18 lessons, 240 minutes. Individually €399 net per person, also as an add-on to the subscription.
Yes. “Planning and Assessing Restore Tests” shows, based on BSI Standard 200-4, IT-Grundschutz module CON.3, ISO/IEC 27001 Annex A, ISO 22301 and DORA, how to derive a test concept from recovery time and tolerable data loss, run tests safely in isolation, measure the time until the system is actually usable and have the result signed off by the business. A case workshop after a ransomware attack and six templates, including test plan, test record and business sign-off. 6 modules, 17 lessons, 240 minutes. Individually €399 net per person, also as an add-on to the subscription.
That is what the course “Creating Security Evidence for Customers and Clients” is for. From the perspective of the service provider being assessed, it shows how to classify requirements under ISO/IEC 27001, ISO/IEC 27036, Section 30 BSIG and DORA, build a reusable security profile and evidence register, word answers robustly using four answer types and release them in a controlled way – without unsupported commitments. A case workshop with twenty customer requirements and six templates. 6 modules, 14 lessons, 180 minutes. Individually €399 net per person, also as an add-on to the subscription. The security profile can then be maintained in the Vercora supplier portal and shared via a link.
Yes. “Access Management and Recertification in Practice” teaches, based on ISO/IEC 27001 Annex A and BSI module ORP.4, how accounts and rights are requested traceably, approved on business grounds, adjusted on role changes and revoked on time, how privileged accounts, service accounts, externals and emergency access are regulated, and how a recertification with business-readable lists works. A case workshop with twelve cases and six templates, including a model access control policy. 6 modules, 15 lessons, 180 minutes. €399 net per person individually, also as an add-on to the subscription.
Yes. “Assessing and Treating Information Security Risks” teaches the methodology based on the structure of ISO/IEC 27001 (6.1.2 and 6.1.3), ISO/IEC 27005, BSI Standard 200-3 and DORA: scenarios instead of keywords, described scales, separate gross and net assessment, controls credited only with evidence of effectiveness and risk acceptance with decision-maker, justification and deadline. A case study with five scenarios leads through to a decision paper for management. 7 modules, 20 lessons, approx. 7 hours, seven templates. €399 net per person individually, also as an add-on to the subscription.
Yes. “Conducting Internal ISMS Audits in Practice” teaches the methodology based on the structure of ISO/IEC 27001 (clause 9.2), the ISO 19011 guideline, BSI IT-Grundschutz and the DORA requirements for internal audit: audit assignment and independence, risk-based planning, interviews and sampling, assessing evidence and findings that hold up. A continuous case on access management leads through to the report and the effectiveness review. 7 modules, 21 lessons, approx. 7 hours, seven templates. €399 net per person individually, also as an add-on to the subscription.
Yes. “AI in Everyday Work” is a 90-minute online course for all employees who use generative AI: classifying data correctly, checking results, recognising attacks such as hidden instructions or cloned voices, labelling under Art. 50 AI Act and reporting channels. Art. 4 AI Act obliges companies that use AI to take measures to foster the AI literacy of their staff; since 27 July 2026, the version amended by Regulation (EU) 2026/1744 applies, which requires appropriate measures but no specific level of competence. The course is such a measure and ends with a verifiable certificate of attendance. It is included in the base package, from €17 net per employee per year.
Yes. The online course “Incident Response and Playbooks” guides you through the process according to NIST SP 800-61 and ISO/IEC 27035, embedded in BSI Standard 200-4: prepare, detect, contain, eradicate, recover and learn. It covers the reporting obligations under Section 32 BSIG (24 hours, 72 hours, one month), Art. 33 and 34 GDPR and DORA, contains five playbooks, for example for ransomware and data exfiltration, and three role tracks for first responders, responders and crisis teams. 8 modules, 35 lessons, approx. 7.5 hours. €499 net per person individually, also as an add-on to the subscription.
All courses run on the Vercora training portal. It shows participation, completions and certificates per person, creates a management report as PDF and flags refreshers due according to the chosen interval of 6, 12, 24 or 36 months. Every certificate is numbered and can be checked online for authenticity; participant lists are available as PDF and CSV.
Yes. For every course you can book a 60-minute live office hour for €290 net, for up to 5 participants. If you want to tackle a topic together, such as a business impact analysis or the classification of an outsourcing arrangement, there is the 3-hour live workshop for €890 net including preparation and a results report. Subscribers get an allowance of 5 office hours for €1,290 per year.
Yes, the role-based and specialist courses are also available as single seats with 12 months of access, for example the NIS-2 management training for €249 net. Courses for all staff are only available in the base package.
The subscription runs for 12 months; single seats are valid for 12 months including updates. All courses are available in German and English.
Request a quote
Choose a package, an add-on or a single seat and tell us the number of your employees or participants. You will receive a quote; after booking, the office sets up access to the training portal.
Several packages, add-ons or a live session? Name the course and topic in your message.
The courses are independent offerings of Sachverständigenbüro Schulte and are not certified or approved by the BSI. No legal advice.
Your contact: Heinrich Markus Schulte
IT expert witness and IT auditor with 30 years of hands-on IT experience. Examines IT the way supervisors and statutory auditors do.