Fundamentals and threat landscape
Event, incident and crisis, life cycle, roles and CIRT, legal framework
Home / Training / Incident Response and Playbooks
New · NIST SP 800-61 · ISO/IEC 27035 · BSI Standard 200-4
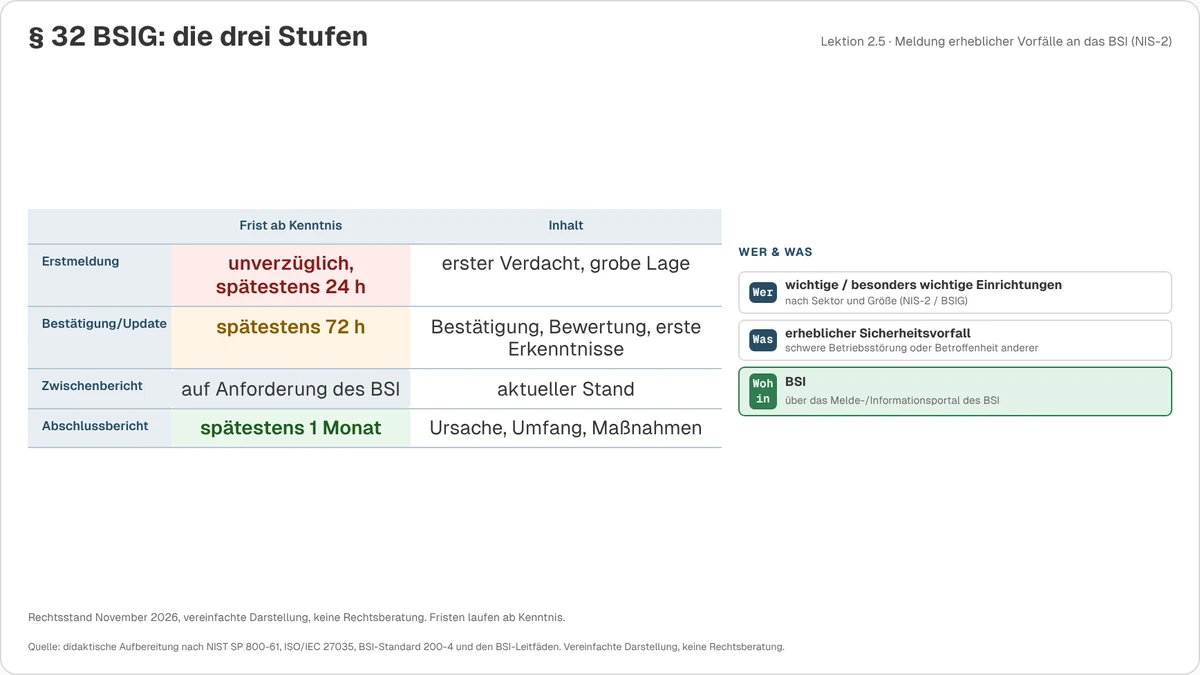
Ready to act in an emergency: the course turns the handling of IT security incidents into routine, from the first alert to the lessons-learned review. With three switchable role tracks for first responders, responders and crisis teams, five scenario-based playbooks and the reporting obligations under Section 32 BSIG, GDPR and DORA. For IT emergency teams and CSIRTs, IT service and digital first responders, IT management and CISOs, crisis teams and management, and data protection officers.
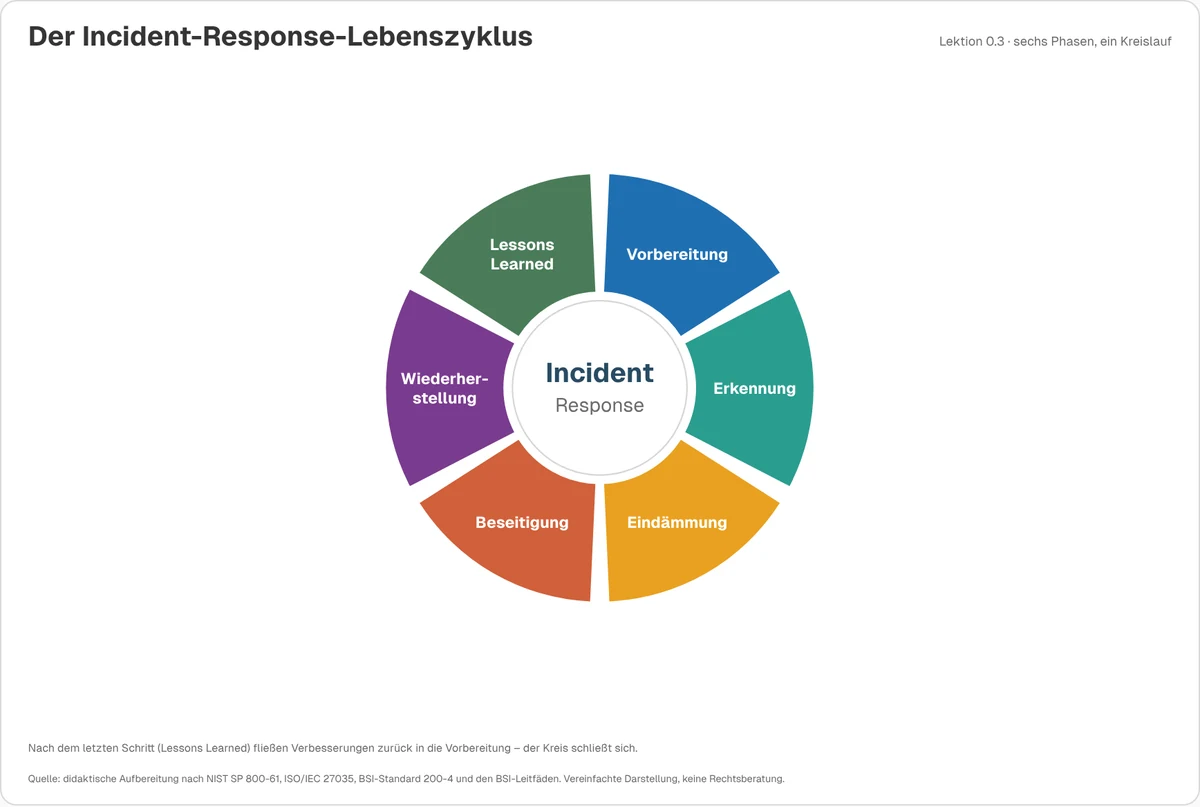
Anyone who only thinks about whom to call, what to switch off and which deadline is running once an incident occurs loses the decisive first minutes. The course guides you through the six-phase life cycle according to NIST SP 800-61 and ISO/IEC 27035, embedded in BSI Standard 200-4.
Every step becomes concrete: disconnect instead of switching off, secure evidence, determine scope and severity, eradicate first and then recover, and trigger the statutory reports in parallel. The five playbooks translate the process into procedures for the most common emergencies.
Event, incident and crisis, life cycle, roles and CIRT, legal framework
Policy, IR plan, playbooks, RACI and escalation, logs, backups, IT emergency card
Severity, immediate measures, preservation of evidence, Section 32 BSIG, GDPR and DORA
Forensics and chain of custody, containment, eradication, recovery, crisis communication
Ransomware, phishing and CEO fraud, data exfiltration, DDoS and account takeover, insider threats
First responders, responders, crisis team, lessons learned, metrics and final test
Incident response in practice: in Vercora you record incidents with their reporting history under NIS-2, GDPR, DORA and CRA – exactly the process the course teaches. You can additionally practise the emergency in the NIS2 tabletop exercise, and prepare recovery with Emergency Management and BCM .
Auditor’s view
“In an emergency, what matters is not the thickest concept but who does the right thing in the first minutes – and that can be practised in advance.”
Heinrich Markus Schulte · IT auditor and expert witness
Brochure as PDF (4 pages, German, 510 KB)
How to book: Individually without a subscription: €499 net per person, 12 months of access. As an add-on to the subscription at the same price per person. Complements the NIS-2, CRA and BCM courses.
Live Add live: Office hour 60 min. for your questions, €290 · workshop 3 hrs, e.g. setting up an IR plan with roles, escalation and reporting channels for your organisation, €890
Request a live sessionCompany-wide licence, white label and operation on your own web space on request; test access and demo on request. Basis: NIST SP 800-61, ISO/IEC 27035, BSI Standard 200-4, Section 32 BSIG, Art. 33 and 34 GDPR and DORA, legal status November 2026. Training on the procedure, not legal advice. “BSI” is a trademark of the BSI.
Related
Single seat, annual subscription or training package
Together we put together a training package that fits your responsibilities and your qualification needs. All courses run on the Vercora training portal, with knowledge checks and a certificate of attendance that can be verified online.