Member of BISG e. V. · Düsseldorf +49 151 12479963sachverstaendiger@itschulte.deVercora login

Home / Training / SIEM use cases

NIS2 · DORA · ISO/IEC 27001 · ISACA guide

SIEM use cases: attack detection training with evidence

The online course that helps IT governance and IT operations master security use cases and manage their attack detection with evidence. Based on the guide “Security Use-Cases – ein Katalog” by ISACA Germany Chapter e. V., linked to MITRE ATT&CK® and BSI IT-Grundschutz.
Catalogue
42 use cases
Lessons
63
Knowledge checks
61
Duration
approx. 4.5 hrs
Pass mark
from 75%
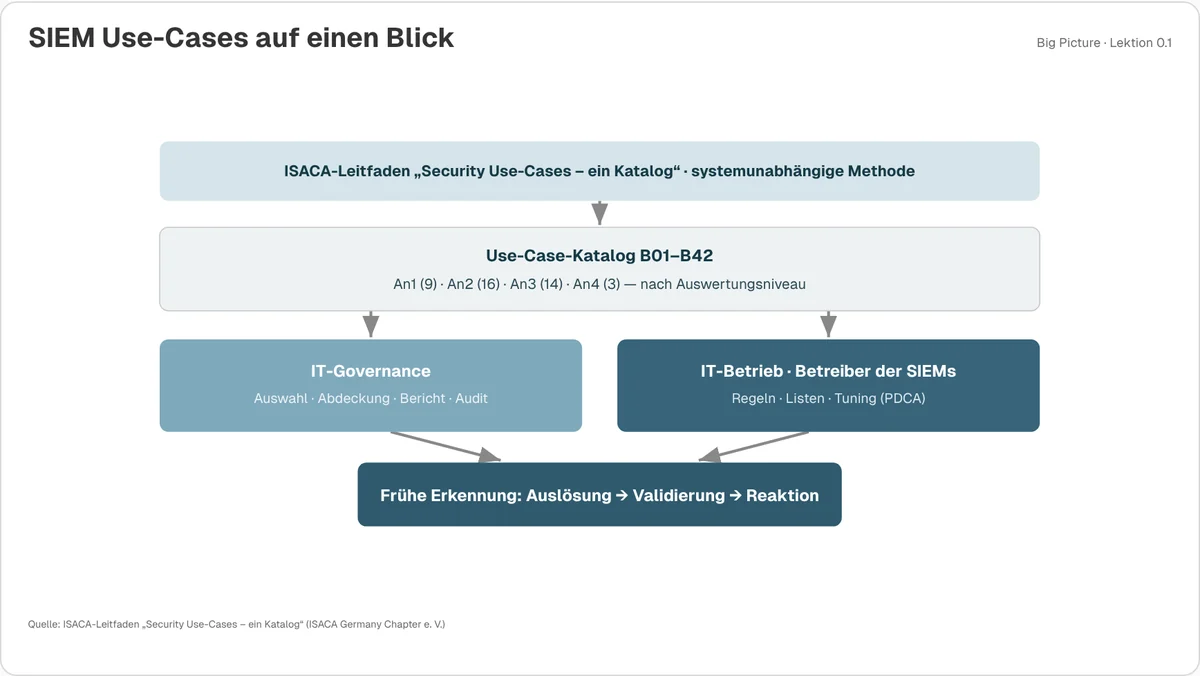
SIEM use cases at a glance: the ISACA guide provides the use case catalogue B01 to B42 by analysis level An1 to An4; IT governance manages selection, coverage, reporting and audit, IT operations handles rules, lists and tuning; the goal is early detection with triggering, validation and response

Why attack detection is mandatory

Operators of critical facilities must use attack detection systems under Sec. 31(2) BSIG. For important and essential entities, handling security incidents is one of the risk management measures under Sec. 30 BSIG. DORA requires financial entities to have mechanisms to detect anomalous activities (Art. 10), and ISO/IEC 27001 requires monitoring of networks, systems and applications (Annex A, control 8.16).

Auditors and supervisors ask not only whether a SIEM is running, but which use cases it covers, why, and who manages it. That is exactly what the course teaches.

Who it is for

  • IT governance, information security officers and auditors: select use cases, manage coverage, run reporting and audits
  • IT operations and SOC: events, rules, lists and tuning, with scripts and a log code reference
  • Management: understand the obligation, risk and evidence of attack detection

Your benefits

  • Provide evidence: certificate of attendance verifiable online, plus reporting and evidence templates with coverage matrix and audit checkpoints
  • Audit-proof documentation: coverage per asset class and use case, justified deviations, recertification and action plan
  • Enable your team right away: event codes, rule language, allow and deny lists, tuning, with PowerShell and Linux examples
  • Vendor-neutral: method, not product marketing, applicable to any SIEM
Method

Levels, landscapes, coverage

Analysis levels An1–An4, IT landscapes L01–L05, ATT&CK coverage

Operation

Rules, lists, tuning

Event codes, rule language, allow and deny lists, tuning, profiles

Catalogue

All 42 use cases B01–B42

As profiles, plus reporting and audit templates and references

References

BSI, MITRE ATT&CK®, log codes

BSI modules, ATT&CK reference with Navigator link, Windows/Linux reference with more than 400 audit events
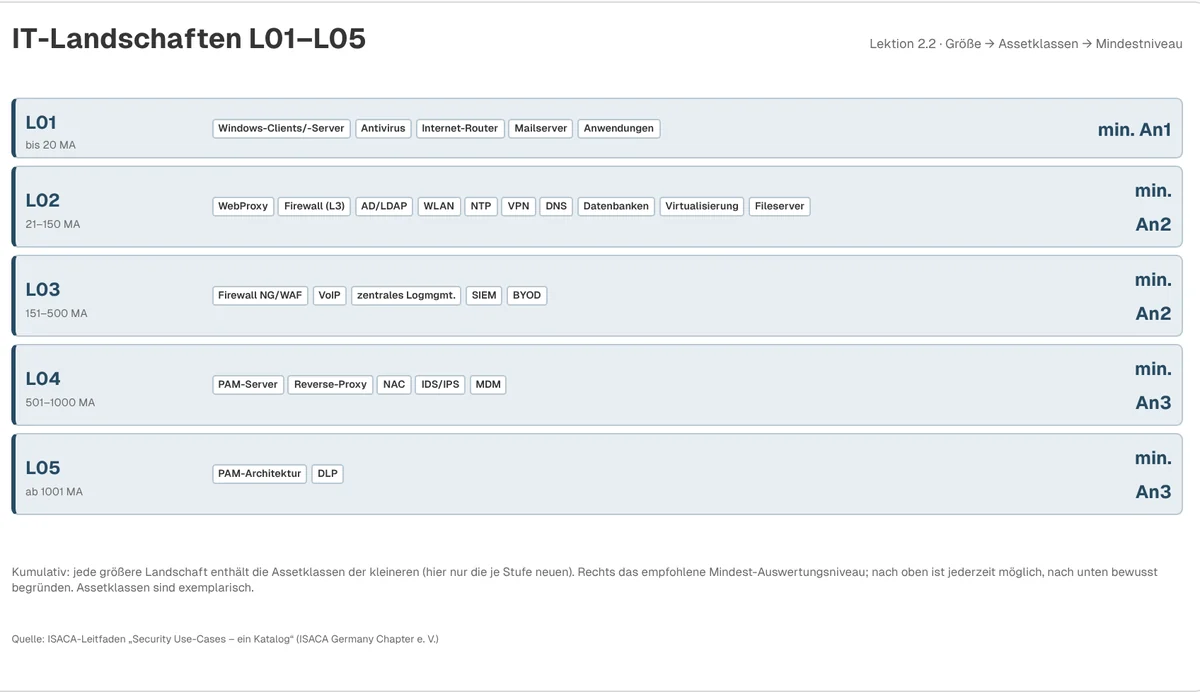
IT landscapes L01 to L05: from up to 20 to more than 1,000 employees, typical asset classes per level and the recommended minimum analysis level An1 to An3
Size, landscape, level. Which analysis level fits your IT landscape.
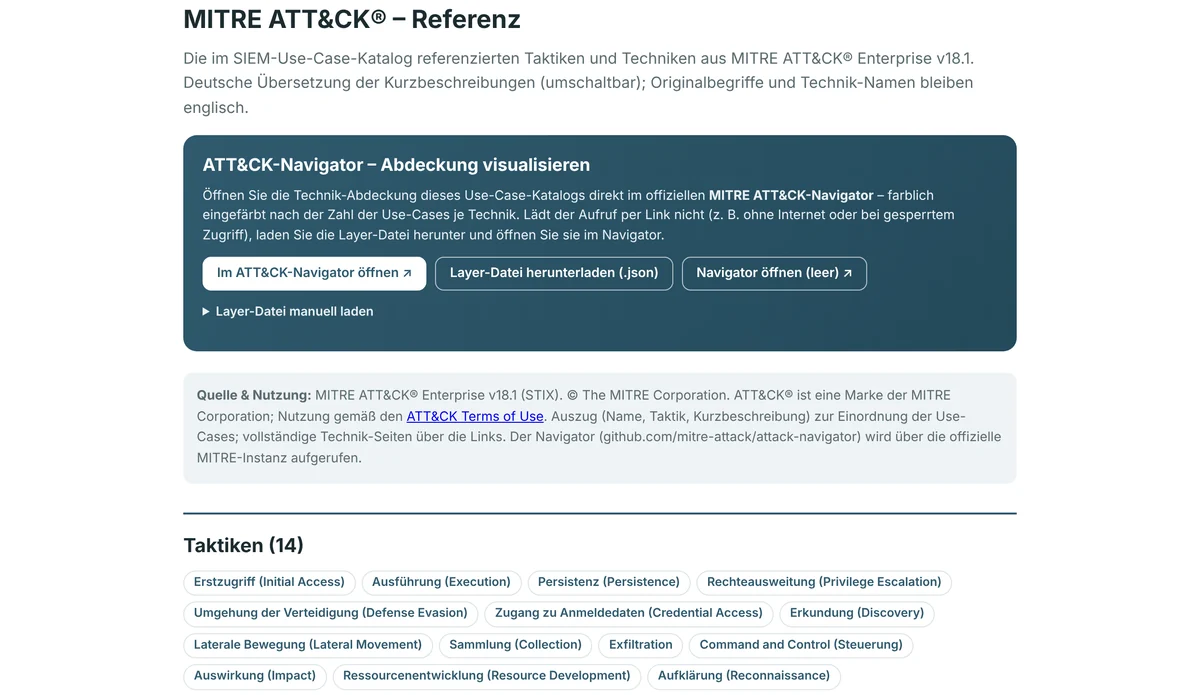
The course's MITRE ATT&CK reference with a link to the ATT&CK Navigator to visualise coverage, and the 14 tactics
MITRE ATT&CK reference. Visualise use case coverage in the Navigator.
Reporting and evidence form on use case coverage with cover sheet, metrics, recertification, measures and regulatory mapping
Audit-ready evidence form. Coverage, metrics and measures as a template.
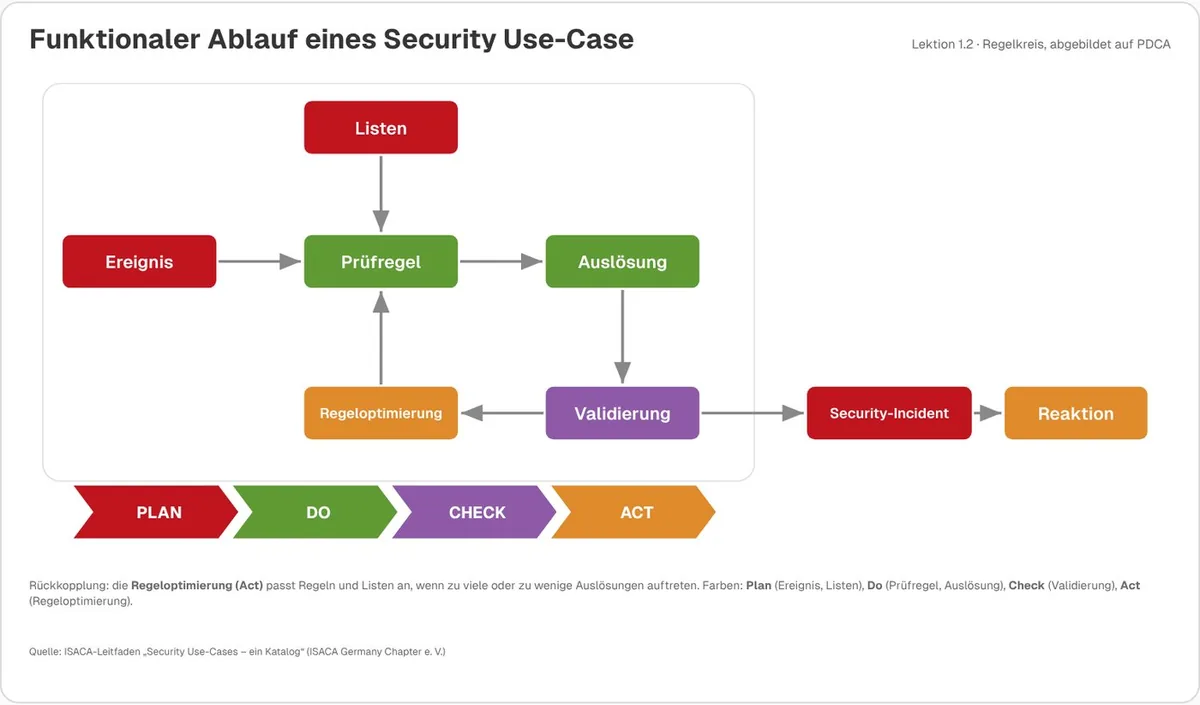
Functional flow of a security use case as a control loop: event and lists feed into the rule, trigger, validation, security incident and response, with feedback via rule optimisation in the PDCA cycle
Flow of a use case. From the event to rule optimisation.
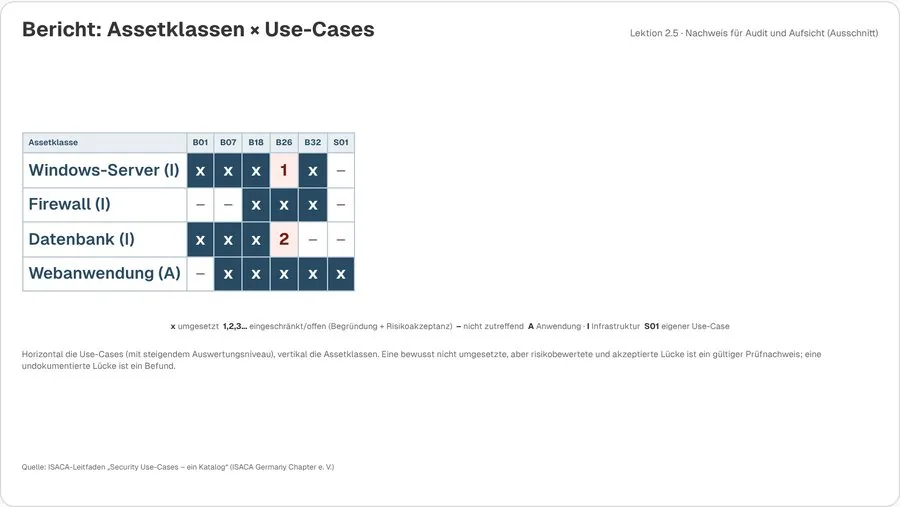
Report asset classes by use cases: matrix showing coverage per asset class such as Windows server, firewall, database and web application
Coverage matrix. Asset classes and use cases in the report.
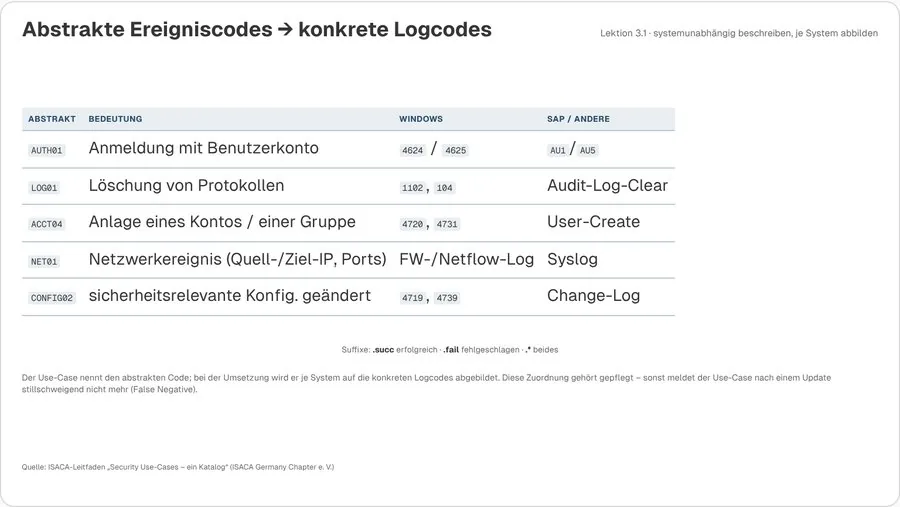
Table of abstract event codes and concrete log codes for Windows and SAP, such as logon, deletion of logs, account creation and configuration change
Event codes and log codes. Describe system-independently, map per system.

Evidence: numbered certificate of attendance, verifiable online. It proves attendance; it is not a certification of SIEM operations and not an audit attestation.
Heinrich Markus Schulte

Auditor’s view

“In audits I rarely see missing technology, but often missing justification for why exactly these use cases run and others do not.”

Heinrich Markus Schulte · IT auditor and expert witness

Questions supervisors and auditors ask

  • Which use cases are the minimum for your IT landscape, and why?
  • How is the effectiveness of the rules tested and documented?
  • Which ATT&CK® tactics are not covered, and who accepted that?
  • How often are rules, lists and exceptions reviewed?

Brochure as PDF (4 pages, German, 550 KB)

How to book: As an add-on to the subscription for €790 net per year (up to 5 people). Single seat without subscription: €299 net per person, 12 months of access.

Live Add live: Office hour 60 min. for your questions, €290 · Workshop 3 hrs, e.g. prioritise your use cases and map them against MITRE ATT&CK, €890

Request a live session

Company-wide licence and white label on request; trial access and demo available. Based on the ISACA guide “Security Use-Cases – ein Katalog” (ISACA Germany Chapter e. V.). MITRE ATT&CK® is a trademark of the MITRE Corporation. Not legal advice.

Related

More courses for these responsibilities

All 25 courses at a glance → Find courses by target group

Single seat, annual subscription or training package

Talk to us

Together we put together a training package that fits your responsibilities and your qualification needs. All courses run on the Vercora training portal, with knowledge checks and a certificate of attendance that can be verified online.