A
GRC as a Service
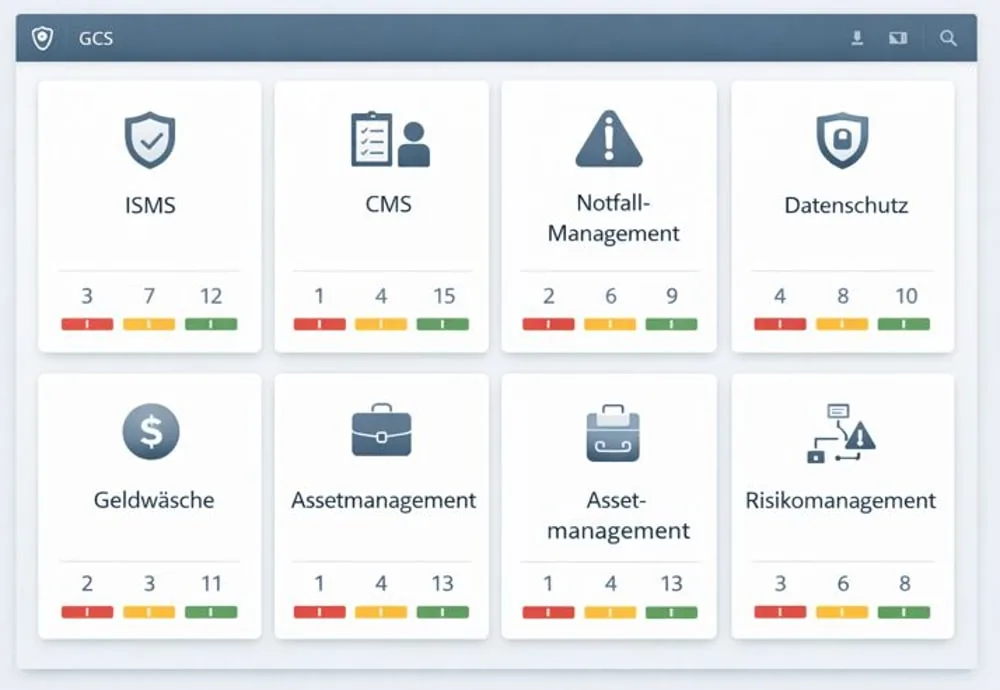
Central platform for risks, controls, policies and measures, with audit preparation, vendor risk workflows and continuous monitoring.
Added value: real-time audit readiness, one data basis.
Home / GRC, vCISO & BCM
COMPLIANCE. SIMPLY. DONE.
Holistic compliance and security solutions for regulated companies, with one central contact, clear responsibilities and audit-ready processes.
THE SITUATION
ISO 27001, GDPR, MaRisk, MiFID II, DORA, NIS2 and sector-specific supervision meet structures that were not built for them.
SERVICE MODULES
A
Central platform for risks, controls, policies and measures, with audit preparation, vendor risk workflows and continuous monitoring.
Added value: real-time audit readiness, one data basis.
B
Professionally qualified compliance officer under the MiFID II Delegated Regulation, MaRisk, KAMaRisk: CMS, legal inventory, reports to management and supervisors, training.
Added value: legal certainty without internal overload.
C
Security strategy, setting up and running the ISMS, risk-based prioritisation, support during audits and security incidents.
Added value: expert access without a full-time position.
D
BCM under ISO 22301 and BSI 200-4: business impact analyses, emergency and recovery plans, tests and exercises, integration with incident response.
Added value: proven emergency processes, demonstrable resilience.
YOUR ADDED VALUE
PRICING MODELS
All packages can be extended modularly.
Smaller regulated companies and entry projects
from €2,500 / month
Financial service providers and regulated mid-sized companies
from €4,500 / month
Critical companies with high supervisory requirements
from €6,500 / month
All prices net plus statutory VAT. Reserved services are provided by the partner firms RA Reinknecht, WPNO AG and Dürkop Möller und Partner mbB.
FREQUENTLY ASKED QUESTIONS
A virtual Chief Information Security Officer takes on responsibility for information security as an external expert: strategy, setting up and running the ISMS, risk-based priorities and support during audits and security incidents, without you having to fill a full-time position.
Yes, as an external information security officer, as an external data protection officer and as a professionally qualified compliance officer under the MiFID II Delegated Regulation, MaRisk or KAMaRisk.
Through predictable monthly fees from €2,500 net. All packages can be extended modularly, so you can start with Core Compliance and add security, BCM and reporting as needed.
For regulated companies that have to meet several frameworks at the same time, such as financial service providers, insurers, critical infrastructure operators and regulated mid-sized companies, and that want one central contact instead of scattered responsibilities.
The GRC platform is hosted in the EU. For reserved services I work with the partner firms RA Reinknecht, WPNO AG and Dürkop Möller und Partner mbB.