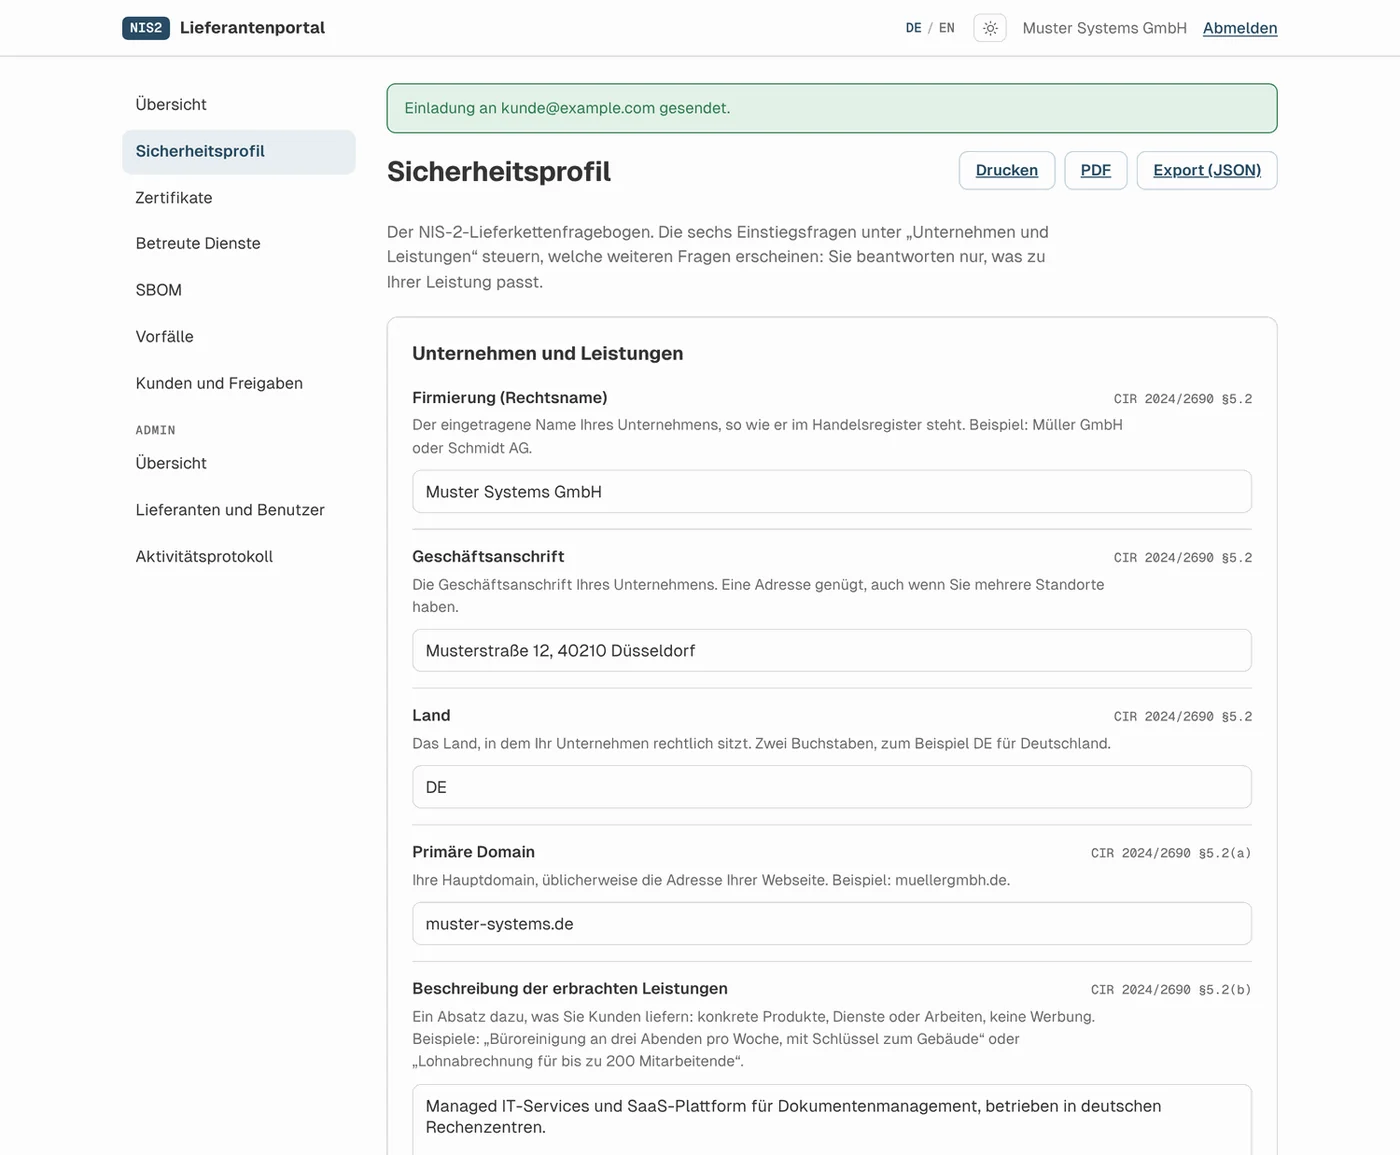
72-field questionnaire
Open data format, 72 fields with legal basis (NIS-2, CIR 2024/2690, GDPR, CRA, DORA) and ISO/IEC 27001 controls. Entry questions hide what does not apply.
Home / Software & Licences / Supplier Portal
Supply chain security evidence · NIS-2 · DORA · CRA
Your suppliers complete the security questionnaire once, 72 fields covering NIS-2, CRA and GDPR plus a dedicated DORA self-assessment, and share their profile with every customer via a personal link: with certificates, SBOM and structured incident and change notifications. A cockpit shows progress and legal-framework coverage. On your own web space or as SaaS in the EU, with no software on the customer side.
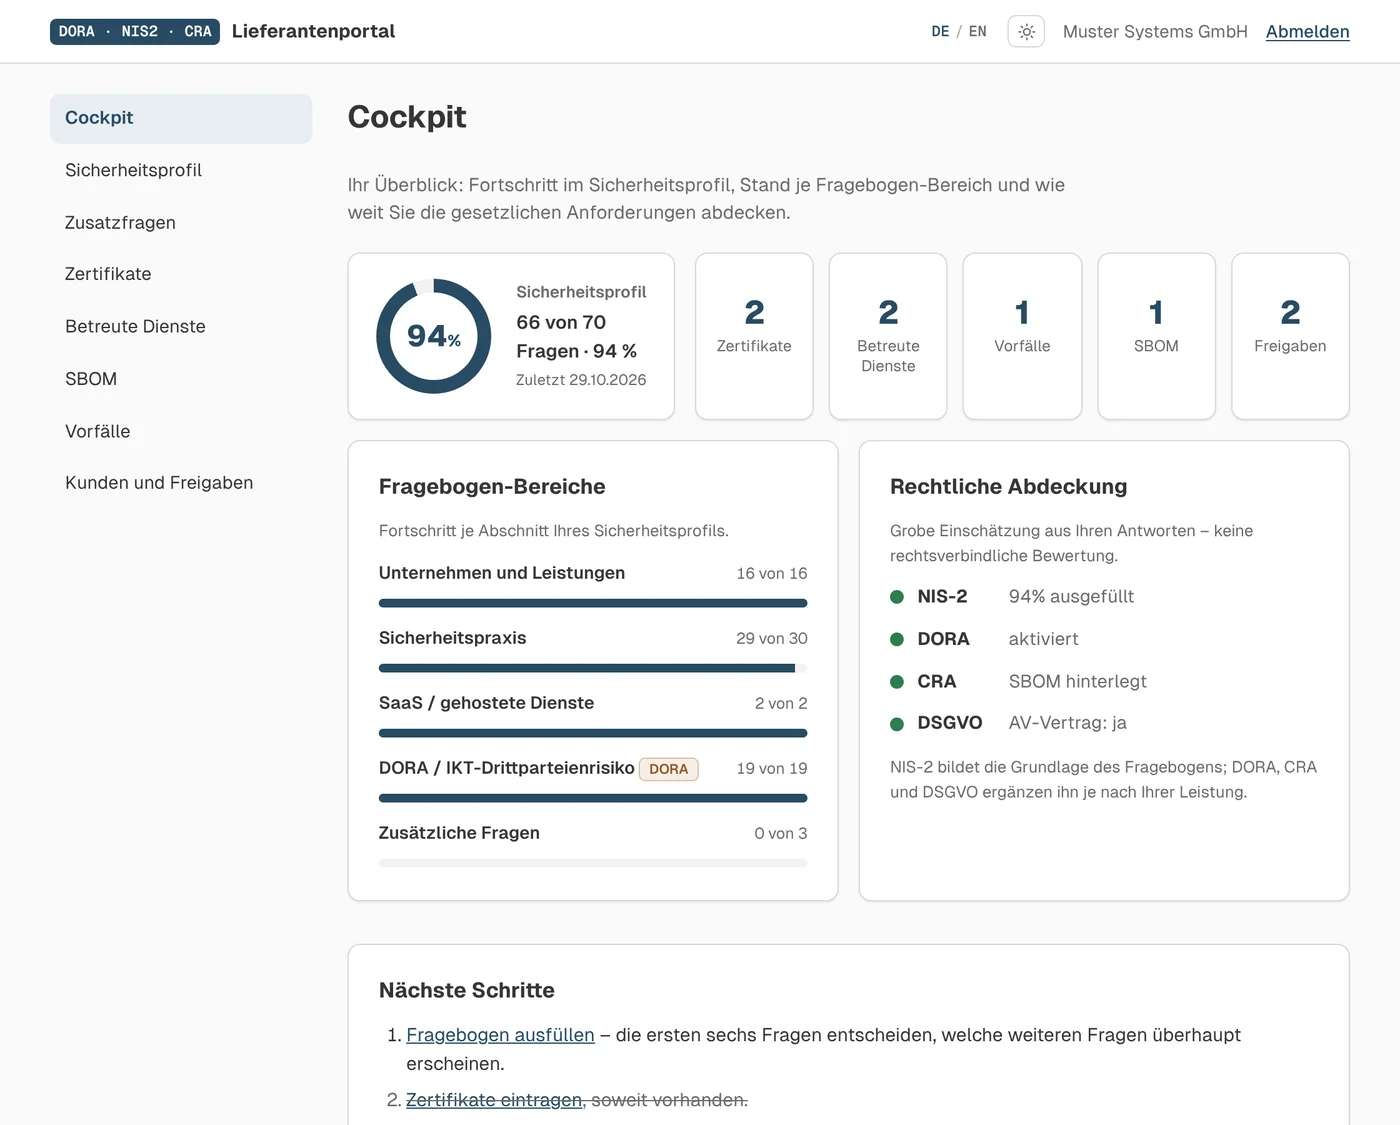
The cockpit: progress per questionnaire section and a traffic light for legal-framework coverage.
Features
From self-assessment to DORA, certificates and SBOM to ongoing communication with the customer: everything in one place, with a traceable log.
Open data format, 72 fields with legal basis (NIS-2, CIR 2024/2690, GDPR, CRA, DORA) and ISO/IEC 27001 controls. Entry questions hide what does not apply.
Self-assessment under Art. 28–30 for ICT service providers of financial customers, CIF flag per share and export of the Register of Information (RoI) under ITS (EU) 2024/2956.
Progress per questionnaire section, key figures on certificates, services and shares, plus a traffic light for coverage of NIS-2, DORA, CRA and GDPR.
ISO 27001, TISAX, SOC 2 with validity dates and managed services, visible to the customer at a glance.
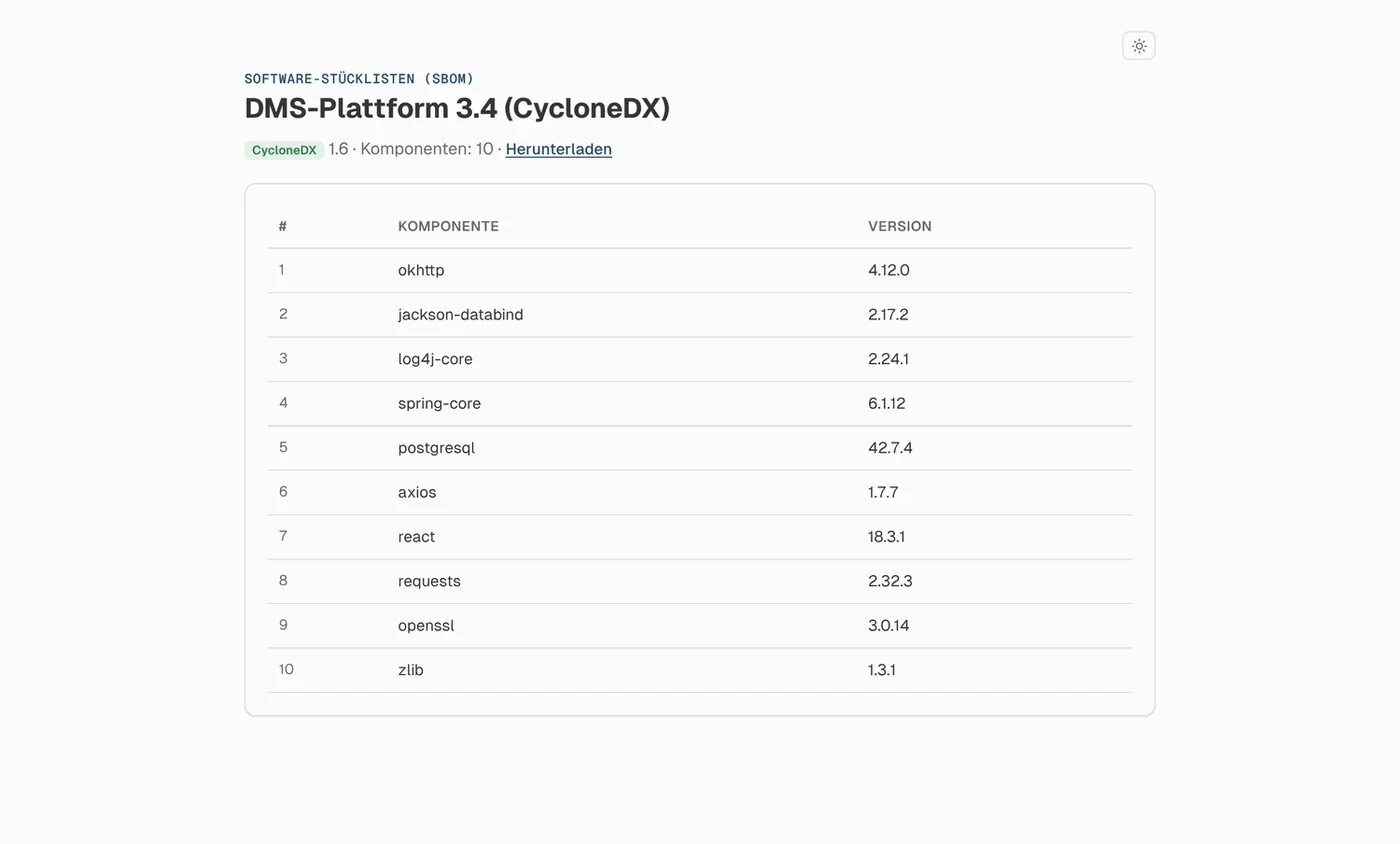
Upload a software bill of materials; the portal detects format, version and components. Customers download it or view the list directly.
Structured by agreed taxonomies: affected systems, services, impacts and end customers, multiple choice plus free text, instantly in the customer view.
Maintain material changes, patch deadlines and updated SBOMs; the customer always sees the current status via their link.
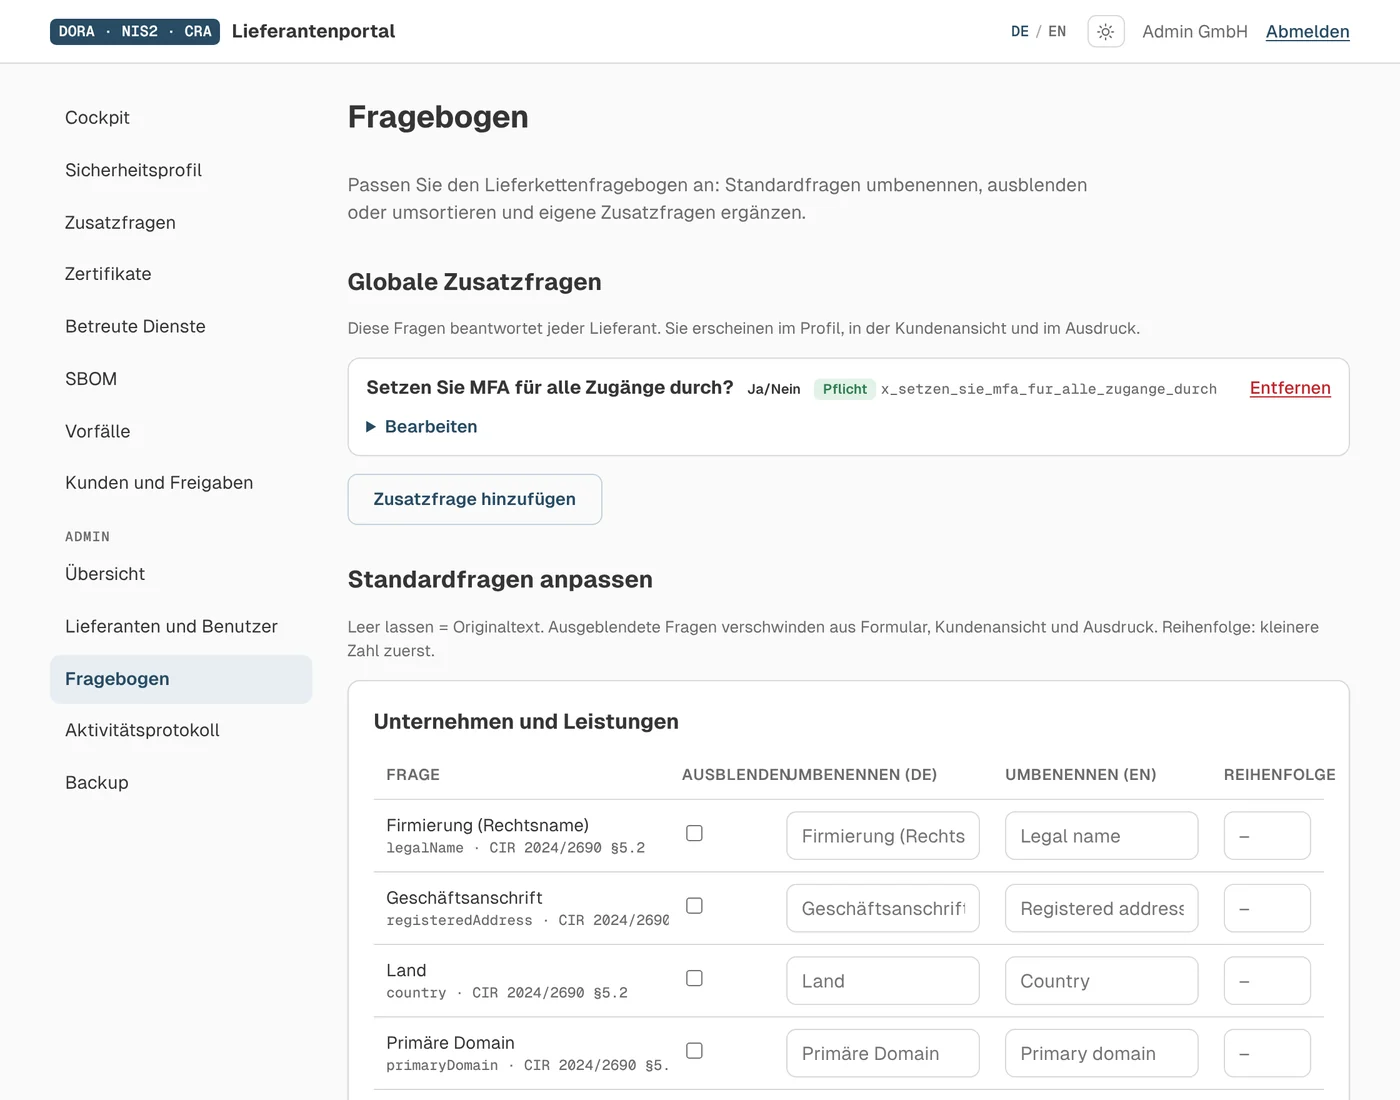
Rename, hide or reorder standard questions and add your own questions: globally, per supplier or by the supplier themselves.
Each customer receives their own 256-bit link to a read-only view. No login, no registration for the customer.
Print the profile, create a PDF and export it as JSON for import into the customer’s GRC or supplier system.
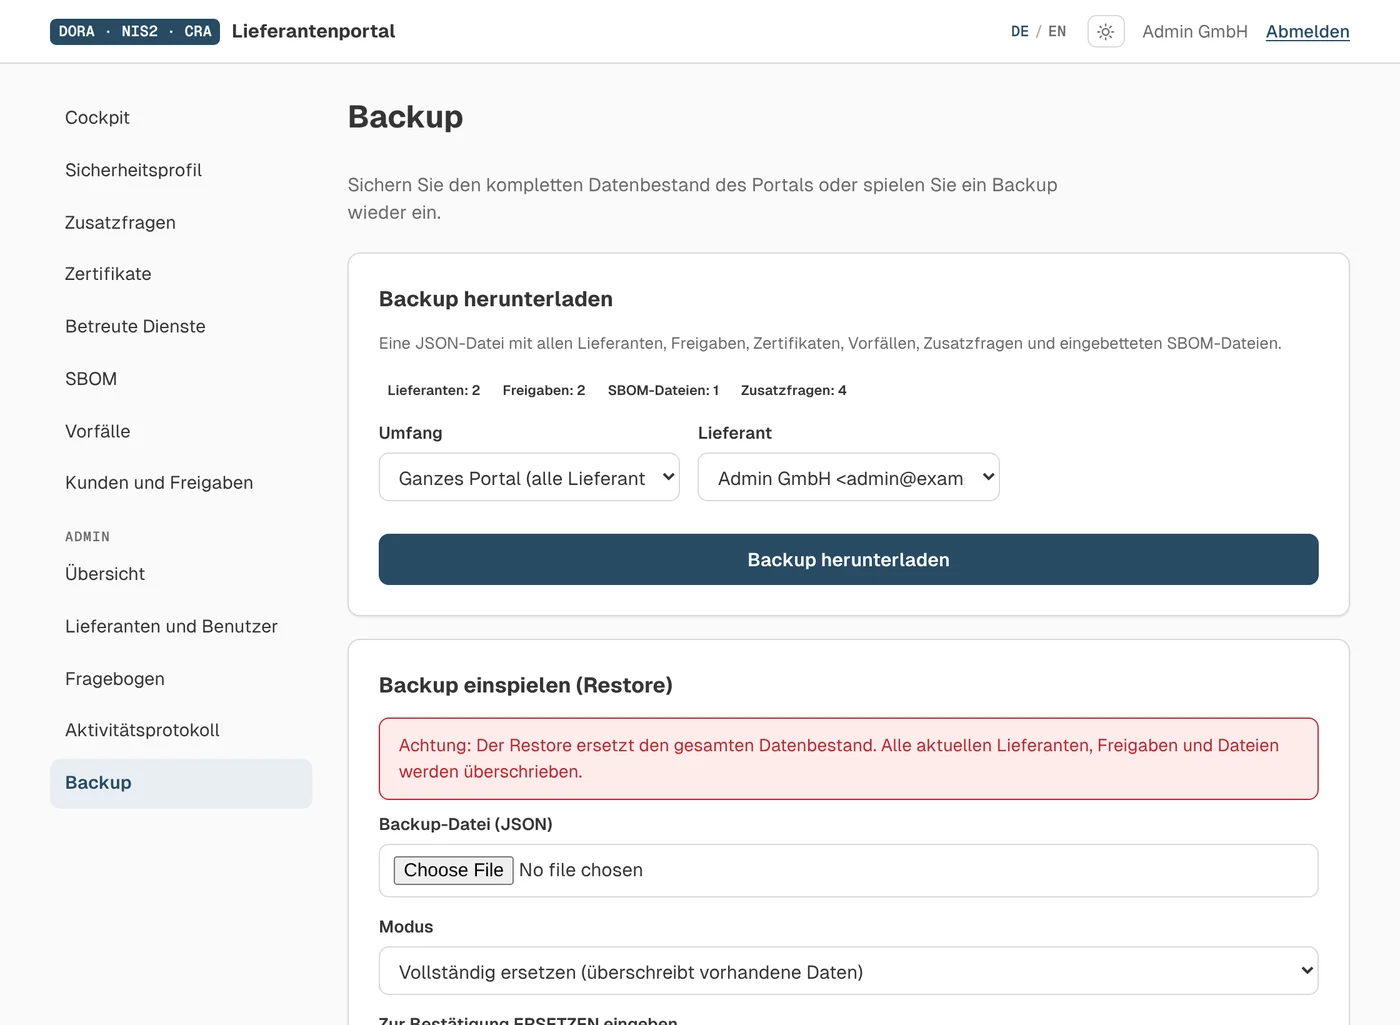
Complete JSON backup including SBOM files, for the whole portal or per supplier. Restore by fully replacing or merging.
Who entered or changed what and when: complete, filterable, audit-proof. Including logins and 2FA events.
Use cases
The portal carries the evidence across the entire lifecycle: at onboarding, when an incident occurs and when something changes. Everything reaches the customer via the same link, without a single email attachment.
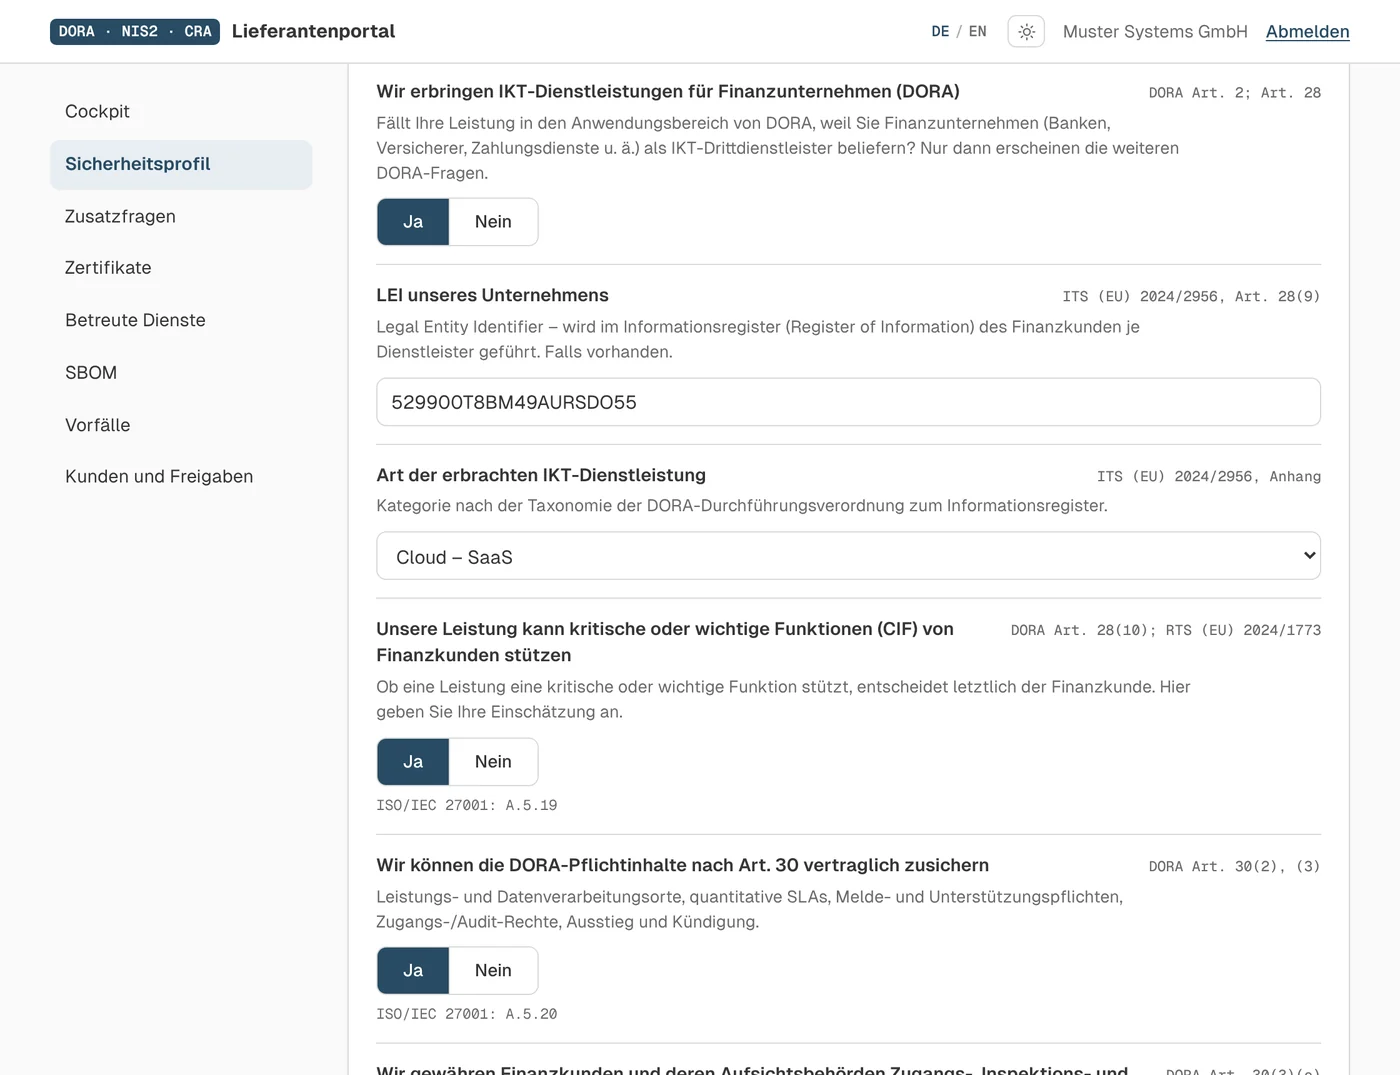
DORA and financial customers
If a supplier serves financial entities as an ICT third-party service provider, an entry question unlocks the DORA section: LEI, type of ICT service, support of critical or important functions (CIF), contractual and audit rights, incident classification, subcontracting chain, RTO/RPO, resilience testing and exit plan.
Legal basis: DORA Art. 28–30 · RTS (EU) 2024/1773 · 2025/532 · ITS (EU) 2024/2956
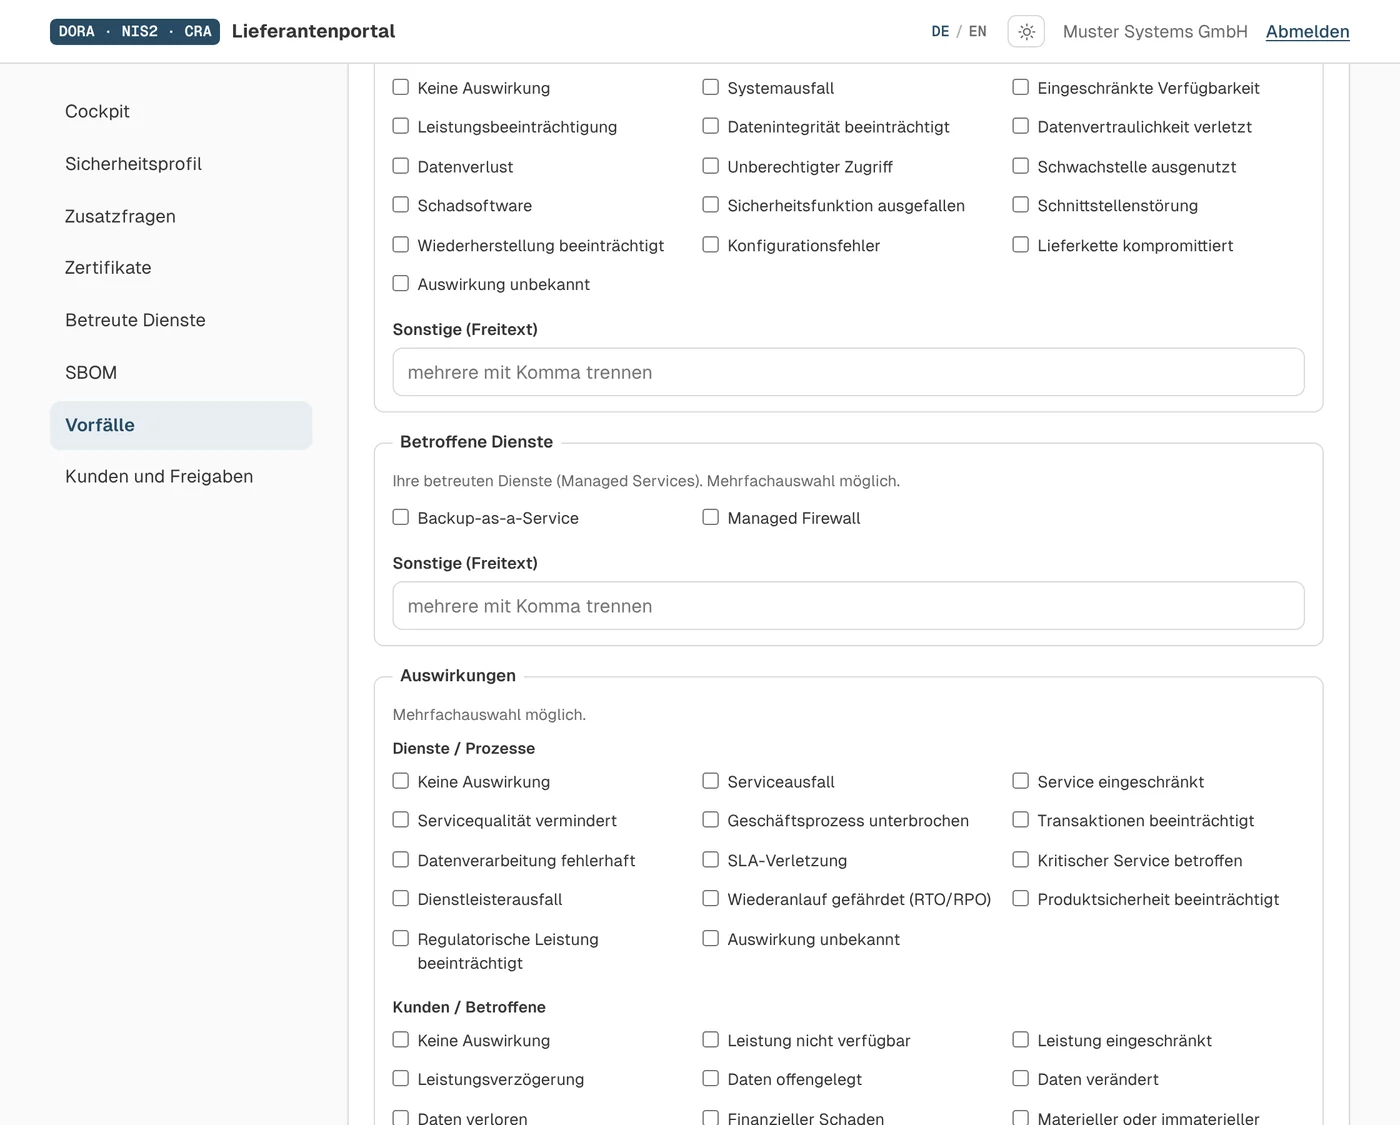
Incident management with the customer
When a supplier publishes a security incident, they select affected systems, services and impacts from agreed taxonomies and add affected end customers and a comment. The incident appears immediately in the view of every connected customer: no mailing list, no forgotten address.
Legal basis: NIS-2 Art. 21/23 · CIR 2024/2690 No. 5.1 · DORA Art. 19 · GDPR Art. 33
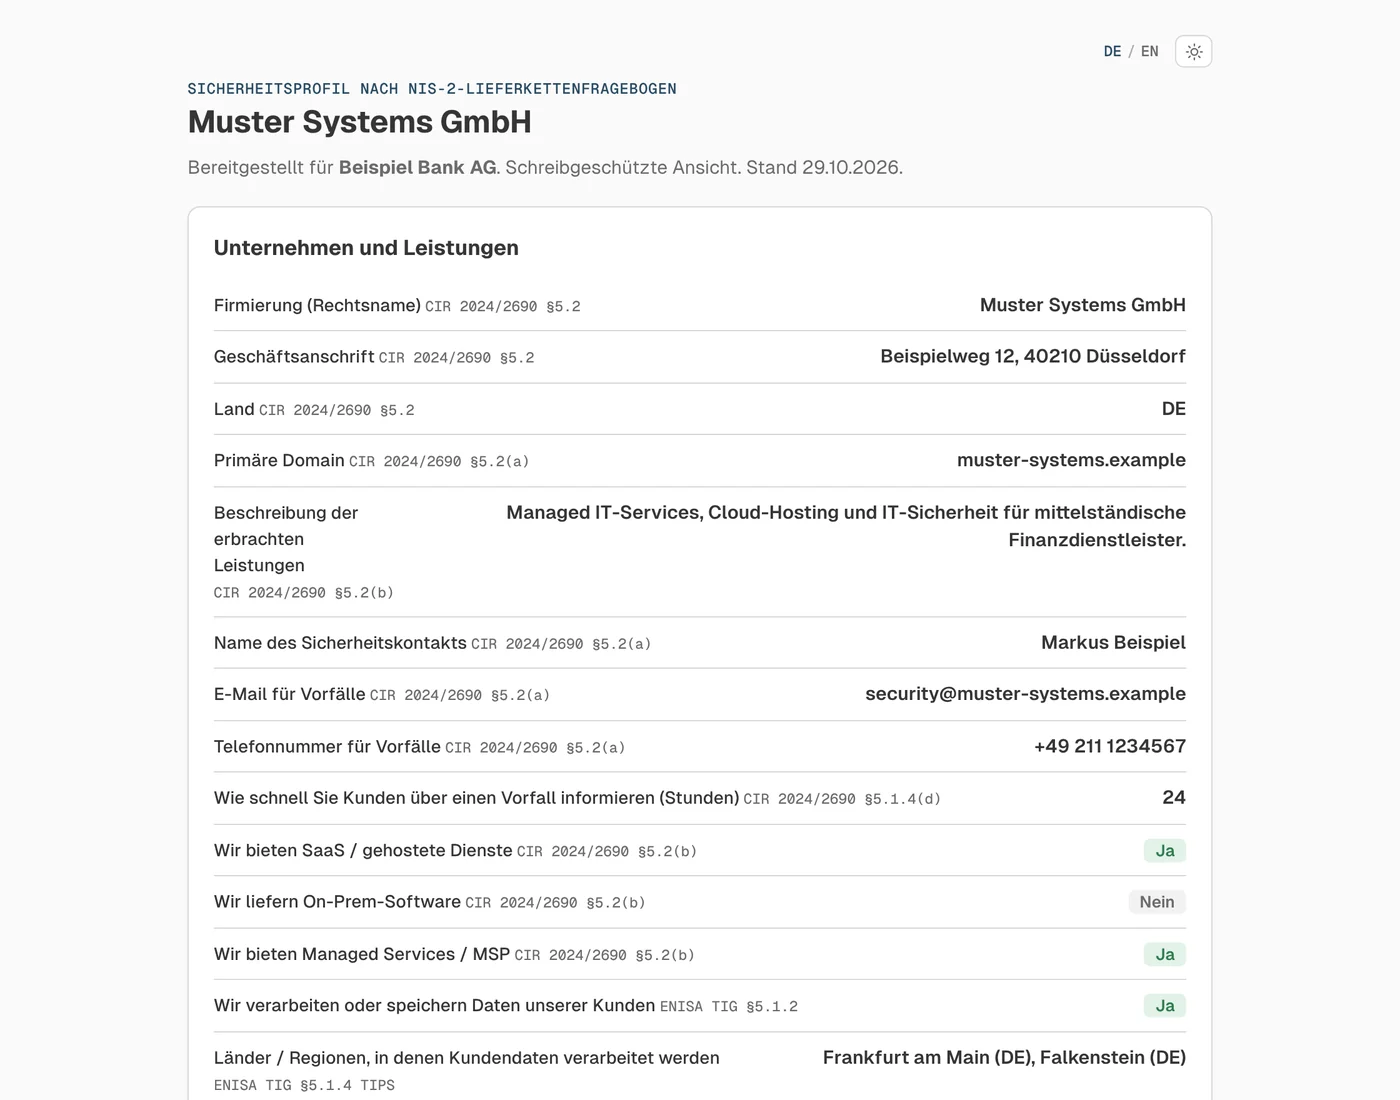
Change management with the customer
If something material changes, such as processing locations, certificates, a new software version or a fixed vulnerability, the supplier enters it once. The current version is immediately visible via the customer’s link, including the new SBOM.
Legal basis: CIR 2024/2690 No. 5.1.4 · CRA Annex I Part II · ISO/IEC 27001 A.8
Register suppliers by invitation code, have them complete the self-assessment and track progress centrally in the cockpit.
Print, PDF, JSON and DORA Register of Information per supplier, with a complete activity log for auditors and supervisors.
The customer exports the profile as JSON and imports it into their GRC or supplier management.
Product tour
Security and data sovereignty
6-digit one-time code by email, stored hashed, failed attempts limited, session ID rotated.
Customer view only via a 256-bit link, “noindex”, rate-limited: no account, no attack surface.
bcrypt hashes, CSRF protection on all forms, rate limits for login, code and reset.
Content Security Policy with nonce, X-Frame-Options, HSTS; internal areas are blocked from the internet.
Everything is stored in one SQLite file, on your web space or on our server in the EU. No external service, plus built-in backup and restore.
pdo_sqlite, openssl and mbstring (standard at IONOS).Roles
Supplier
Customer
Administrator
Licences and prices
Company-wide licence. The price depends on the number of employees, not on the number of users or suppliers.
€590 net
€702.10 incl. 19% VATUpdate fee: €88.50 net per year
€3,400 net
€4,046.00 incl. 19% VATUpdate fee: €510.00 net per year
€4,900 net
€5,831.00 incl. 19% VATUpdate fee: €735.00 net per year
by arrangement
Perpetual licence for the purchased version (option 1). The annual update fee is 15% of the licence cost and covers new versions, questionnaire updates and security updates. With SaaS (option 2), licence and updates are included in the monthly price.
Option 1
You run the portal yourself, for example on your own IONOS web hosting. All data stays entirely with you.
Licence by company size + 15% annual update fee
Option 2
We run the portal for you on servers in the EU. You and your suppliers simply log in, without any technology of your own.
| Employees | per month | per year |
|---|---|---|
| 1–10 | €54.08 | €649.00 |
| 11–1.000 | €311.67 | €3,740.00 |
| over 1,000 | €449.17 | €5,390.00 |
| Special licence | by arrangement | – |
Prices net plus 19% VAT, annual payment in advance.
Go to the hosted portal →Frequently asked questions
No. Each customer receives a personal 256-bit link to a read-only view. No login, no registration, no installation.
72 fields with legal basis covering NIS-2, Implementing Regulation (EU) 2024/2690, CRA and GDPR, each with the matching ISO/IEC 27001 control, plus a dedicated DORA self-assessment under Art. 28 to 30 with Register of Information export.
Both are possible: as a perpetual licence on your own web space (from €590 net plus a 15% annual update fee) or as SaaS hosted in the EU, from €54.08 net per month including licence, updates and hosting.
Yes. The questionnaire editor lets you rename, hide or reorder standard questions and add your own questions, globally, per supplier or by the supplier themselves.
For companies that need to demonstrate the security of their supply chain under NIS2 or DORA, and for suppliers and ICT service providers who want to provide security evidence to their customers without completing a new questionnaire for each one.
Quote and demo
The Supplier Portal can be set up on your web space or used as SaaS and tailored to your suppliers. Request a demo or a quote; on request you receive an invoice instead of online payment.
Developed by a certified expert in information security and IT compliance (CISA, CISM, CIPP/E, CEH). No legal advice.