Home / IT audit for annual financial statements
HGB Sec. 316 · Sec. 316a
IT audit for annual financial statements
Accounting is IT-based, so every statutory audit is also an IT audit. As a CISA-certified IT auditor, I deliver the technical analysis that supports the audit opinion.
AUDIT AREAS
What I audit as part of the statutory audit
ITGC
IT General Controls
Access, authorisations, changes, backup and recovery.
ERP
Application audit
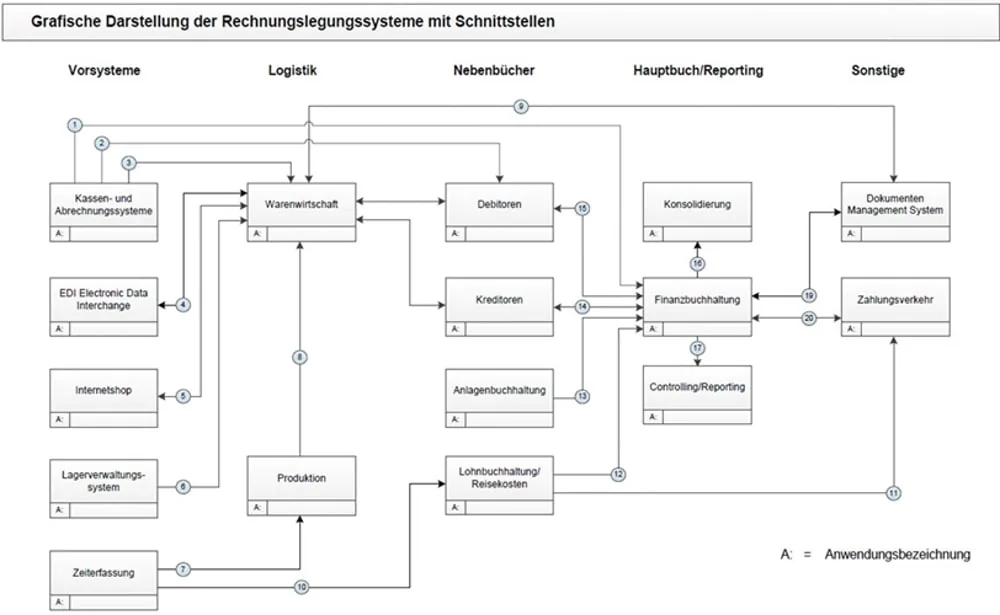
Accounting and ERP systems, interfaces and upstream systems.
PROCESS
Process audit
Accounts receivable, accounts payable and payments.
GOBD
Data security
Integrity and compliance under GoBD.
BCM
IT resilience
Business continuity and recovery capability.
LEGAL BASIS
Who is subject to audit
Medium-sized and large corporations are subject to mandatory audits according to the size classes of Section 267 HGB. The decisive factor is that at least two of the three criteria are exceeded on two consecutive balance sheet dates. Smaller companies can opt for a voluntary audit and benefit just as much.
- Early detection of IT and compliance risks
- Proof of proper accounting to banks, supervisors and investors
- Stronger internal control system and process reliability
Thresholds under HGB as amended since 17 April 2024, applicable to financial years beginning on or after 1 January 2024. Employees as an annual average. Group: net after consolidation, gross before consolidation. EU SMEs under Recommendation 2003/361/EC: employee headcount must be met plus either revenue or total assets.
MY ROLE
IT expert in the audit team
In statutory audits I work as an IT expert or as part of the audit team, not as the statutory auditor. In voluntary audits I act independently.
FOR AUDIT FIRMS
IT audit capacity for your firm, without hiring your own specialists
I support small and medium-sized audit firms during audit season: risk-based, on schedule and documented in the format of your working papers.
Predictable
Fixed allocations for the season, on call for peaks.
Auditor-compliant
Approach in line with IDW PS 330 and ISA [DE] 315, properly documented.
Independent
No consulting for the same client, no conflicts of interest.
“Heinrich Markus Schulte’s deep technical knowledge and regulatory understanding are unmatched. His insights were invaluable for our IT audit.”
Plan the next audit season
Let’s talk about scope, dates and the right model for your company or firm.
Get in touchFREQUENTLY ASKED QUESTIONS
Good to know
Do you replace the statutory auditor?
No. In statutory audits I work as an IT expert or as part of the audit team and deliver the technical analysis that supports the audit opinion. In voluntary audits I act independently.
Which standards do you audit against?
In line with IDW PS 330 and ISA [DE] 315 (revised), supplemented by ISAE 3000, IDW PS 951 and IDW PS 850 as well as GoBD.
How does collaboration with audit firms work?
Through fixed allocations for the audit season and call-offs for peaks. I audit on a risk basis, on schedule and document in the format of your working papers. My profile for audit firms can be downloaded directly.
How do you ensure your independence?
I do not advise any client that I audit in the same context. This avoids conflicts of interest.
Is an IT audit worthwhile even without an audit obligation?
Yes. A voluntary IT audit detects IT and compliance risks early, strengthens the internal control system and provides evidence to banks, supervisors and investors.