PEOPLE · REASON · MACHINE
Audit-ready for DORA, NIS2 and IT audits
Expert, IT auditor, ethical hacker and business continuity manager in one person, with 30 years of hands-on IT experience.
I examine your IT the way supervisors and statutory auditors will, and support you until the evidence is in place.
SERVICES
Audit, protect, stabilise: everything regulated companies need
Not sure where to start? Readiness Check →WHO I WORK FOR
Four starting points, one contact
Choose what applies to you. You go straight to the right service, with prices, process and answers to the most frequent questions.
Banks, insurers & financial service providers
DORA examination readiness, ICT risk management, Register of Information and third-party risk.
DORA-Ready Audit →Audit firms
IT audit capacity in line with IDW PS 330 and ISA [DE] 315, documented in the format of your working papers.
IT audit for audit firms →Critical infrastructure & regulated mid-sized companies
Implement NIS2 with personal coaching and open-isms, plus vCISO, BCM and appointed officer roles.
NIS2 as a Service →Suppliers & ICT service providers
Maintain security evidence for NIS2, DORA and CRA once and share it with every customer via link.
Supplier Portal →How we work together
01
Free initial consultation
30 minutes, bookable online. We clarify the starting point, deadlines and goal.
02
Clear quote
You receive a quote with scope, dates and price, optionally with the fixed-price Readiness Check as an entry point.
03
Implementation with evidence
I work with an auditor’s eye: results that stand up to supervisors, statutory auditors and customers.
ENTRY OFFER
The Resilience Readiness Check
In 5 days you know where you stand, at a fixed price.
OUR OWN PLATFORM
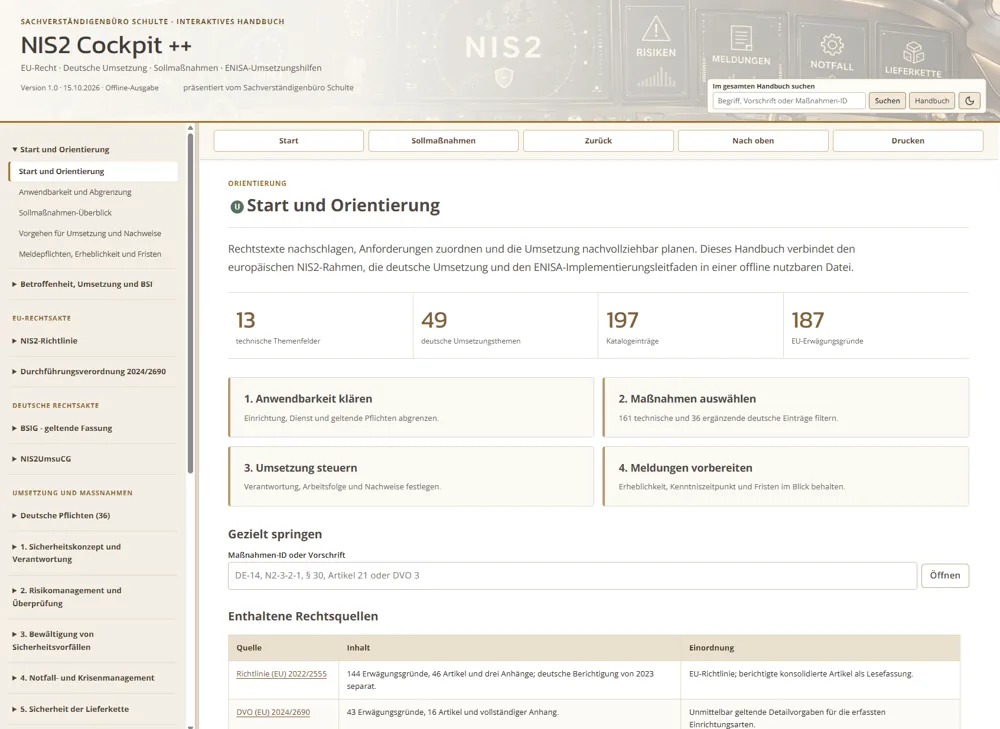
NIS2 Cockpit++: a system instead of a paper flood
Understand legal requirements, check applicability, assess measures and document implementation traceably. Practical, structured, usable offline.
197
measures with legal reference
49
implementation chapters based on ENISA
- Applicability check
- Legal navigator EU + DE
- BSI Grundschutz++
- Reporting obligations & deadlines
- Evidence & reporting
- Template project plan
New · DORA · NIS-2 · CRA
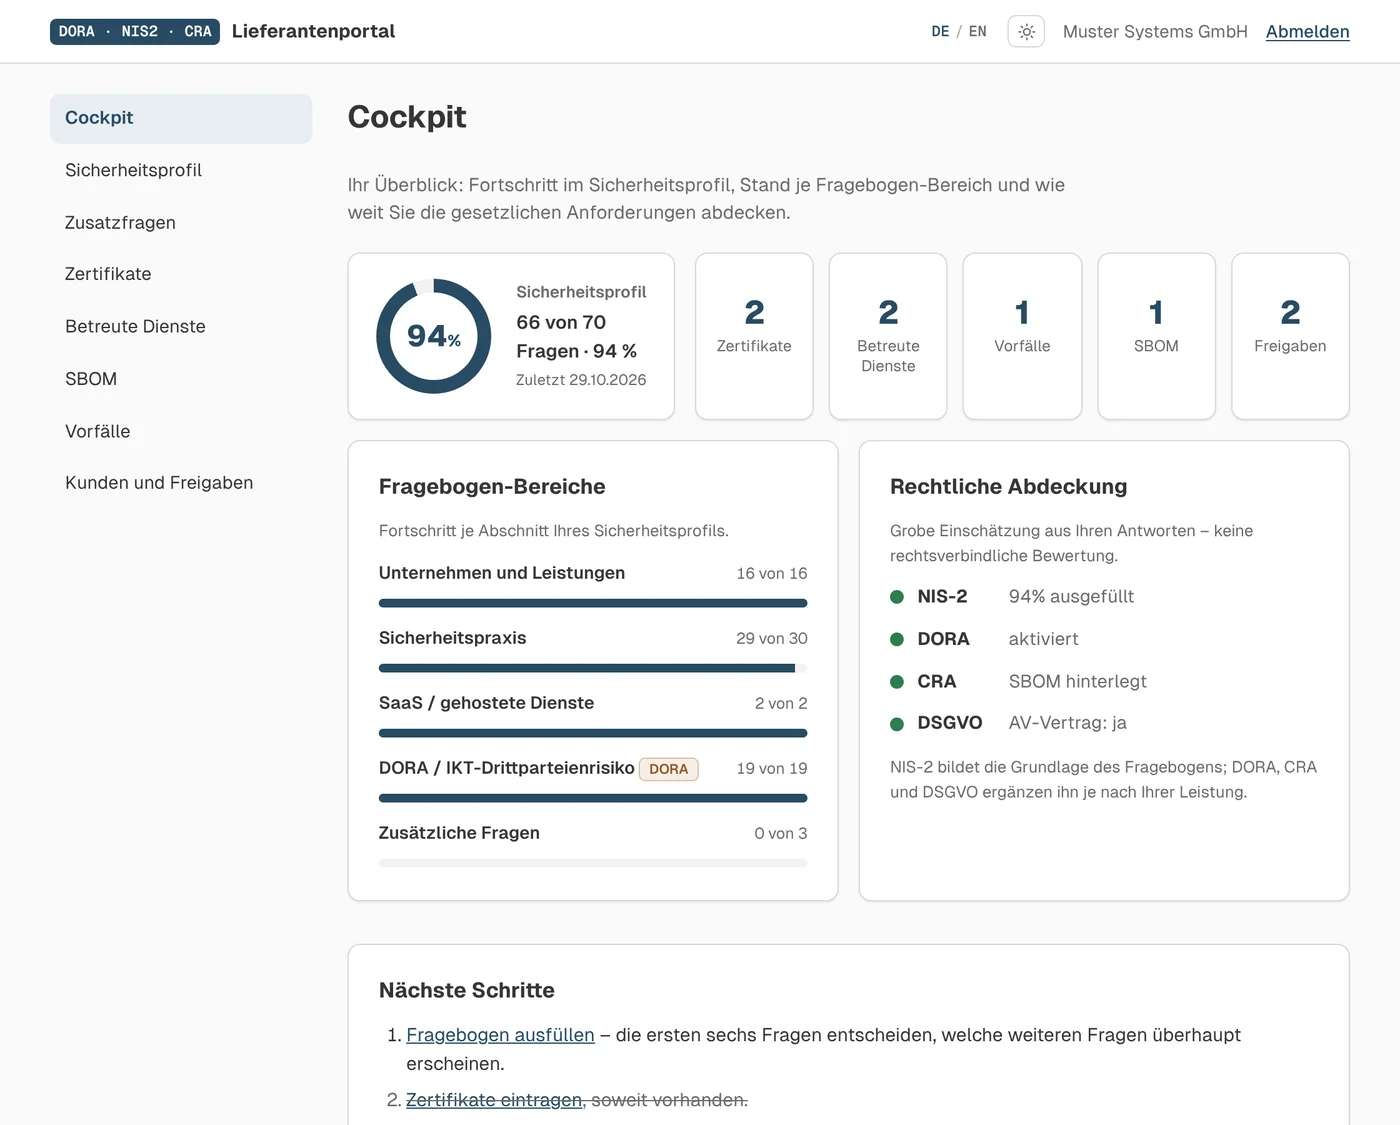
Supplier Portal: security evidence via link instead of questionnaire ping-pong
Suppliers complete the security questionnaire once, 72 fields covering NIS-2, CRA and GDPR plus a DORA self-assessment, and share their profile with every customer via a personal link. With certificates, SBOM and structured incident reports, with no software and no account required on the customer side.
- 72-field questionnaire with legal basis
- DORA module with Register of Information (RoI)
- Cockpit with legal-framework traffic light
- Certificates & SBOM
- Structured incident reports
- Backup, restore & questionnaire editor
IT AUDIT & DIGITAL RESILIENCE
Between finance and technology
My IT audits complement the statutory audit of annual financial statements under Sections 316 and 316a HGB with a sound technical analysis. For banks and insurers I review and confirm business continuity, crisis and recovery plans.
SERVICE PORTFOLIO
Expert office for IT, business continuity and information security
IT Security & Resilience
- IT Security Check
- Testing for security gaps with clear recommendations.
- IT Infrastructure Check
- Analysis of networks, components and failover resilience.
- Vulnerability analysis
- Automated scans and well-founded reports.
Expert Reports & Audits
- Damage assessments
- Professional expert reports on IT and electronics damage.
- Expert witness work
- Impartial evaluations in IT disputes.
- Invoice audits
- Reviewing offers, licences and service provider invoices.
Knowledge & Compliance
- Training & seminars
- Practical training on IT, data protection and security.
- External Data Protection Officer
- Taking on the mandate, GDPR-compliant.
- External Information Security Officer
- As vCISO within GRC as a Service.
WHAT CLIENTS SAY
Trusted by banks, insurers and auditors
“His expertise in implementing DORA ensured that our bank met all new regulatory requirements in an audit-proof and practicable way.”
“Heinrich Markus Schulte’s deep technical knowledge and regulatory understanding are unmatched. His insights were invaluable for our IT audit.”
“… As DORA is closely aligned with international standards (ISO 27001, NIST), you are in good hands with Mr Schulte, as he is an absolute professional in the common information security frameworks.”
Partners who trust us
YOUR CONTACT
Heinrich Markus Schulte
I combine the auditor’s perspective with a deep technical understanding of cyber threats and IT infrastructures. I lead complex IT audits within statutory audits and special audits, with a focus on hardening critical systems and regulatory compliance.
FREQUENTLY ASKED QUESTIONS
Good to know
What do your IT audit services focus on?
On the risk-based audit of IT systems, processes and control structures in line with IDW PS 330, ISAE 3000 and ISA [DE] 315 (revised) as well as GoBD.
How do you support NIS2 and DORA?
With gap analyses, audit preparation, evidence management and information security attestations, for critical infrastructure operators under NIS2 and for the financial sector under DORA.
What is your approach to digital resilience?
I review and confirm business continuity, crisis and recovery plans and test whether the planned recovery times can actually be achieved.
Which certifications do you hold?
CISA, CISM, Certified Ethical Hacker (CEH), ITIL 4 Managing Professional, CIPP/E as well as Lead Auditor & Implementer for ISO 27001, ISO 22301 and ISO 27701 and BSI 200-1 to 4.
What role does the IT auditor play in the auditor’s opinion?
The IT auditor supports the statutory auditor as a subject-matter expert for information systems. They assess IT-supported processes, internal controls and system environments relevant to financial reporting, strengthening the reliability of the audit opinion.
Your next audit is coming.
Let us clarify in 30 minutes where your biggest risk lies. Free of charge and without obligation.