Home / NIS2
NIS2 AS A SERVICE
Implementing NIS2? Software alone is not enough.
I personally support you in introducing and developing an effective ISMS, combining my experience as an IT auditor with open-isms, the open-source ISMS for NIS2.
WHAT YOU GET
Personal coaching instead of anonymous standard consulting
One fixed contact with an auditor’s eye.
The recommended open-source ISMS, included during our collaboration and usable afterwards. More about open-isms
Structured implementation plan with priorities.
Designed to fit your IT operations in practice.
Measures, responsibilities and proof in one place.
With decisions, training and liability questions.
NIS2 COCKPIT++
A system instead of a paper flood
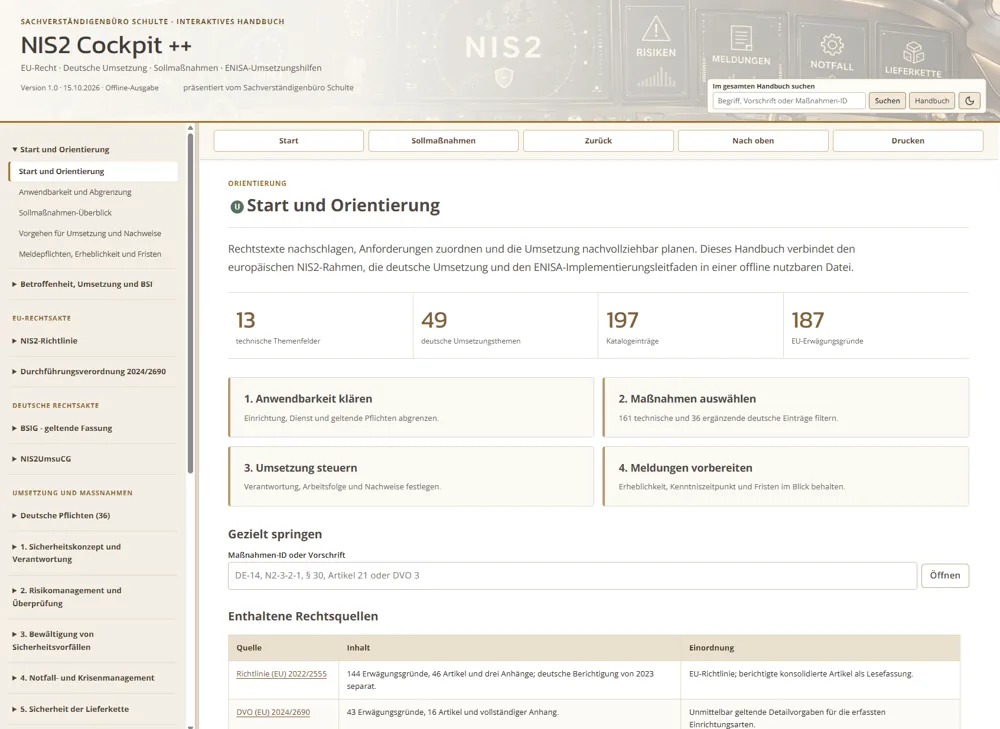
The German-language working platform, usable offline, brings together the NIS2 Directive, Implementing Regulation (EU) 2024/2690, the BSIG and the implementation guidance from ENISA and BSI.
197
measures
49
chapters based on ENISA
100 %
usable offline
The features
Applicability check
Initial assessment by entity type, activity and company characteristics.
Legal navigator
Full-text search across EU and German law including recitals.
Catalogue of measures
197 entries with legal reference and documentable processing status.
BSI Grundschutz++
Assess requirements, implementation status and responsibilities.
Practical implementation
49 chapters based on ENISA, template project plan and evidence recommendations.
Incident response
Reporting obligations, significance and statutory deadlines at a glance.
Evidence & reporting
Analyses, documented assessments, export and backup.
Who is it for?
Companies, consultants and auditors: information security, compliance, IT operations, internal audit.
FREE
NIS2 white paper
Who is affected, which obligations apply and which evidence auditors expect (white paper in German).
For business owners: quickly clarify what lies ahead
In a free initial consultation we clarify applicability, need for action and the scope of support.
Arrange an initial consultationFREQUENTLY ASKED QUESTIONS
Good to know
Am I affected by NIS2?
Sector and size are decisive: as a rule, companies in the NIS2 sectors with 50 or more employees or more than €10 million turnover and balance sheet total are affected; some services, such as DNS services or trust services, regardless of size. An initial classification is provided by the free NIS2 self-check.
What does management have to do?
Management must approve the risk management measures, oversee their implementation and attend training regularly (Section 38 BSIG). It is liable for failures. I support you with decisions, training and liability questions.
Why open-isms instead of spreadsheets and document folders?
Because auditors want to see evidence: in open-isms every requirement gets an owner, a deadline and an approval, and an immutable audit log documents every step. The software is open source, so you keep control of your data.
What does the support cost?
It depends on size and starting point. A clear entry point is the NIS2 Readiness Check at a fixed price from €3,333 net, which is fully credited against an implementation contract.
How do I demonstrate the security of my supply chain?
NIS2 requires the assessment of security-relevant suppliers. With the Supplier Portal suppliers complete a structured questionnaire with a legal basis for each field once and share their profile with every customer.