Principles and roles
Least privilege, need to know; who requests, approves, implements and controls
Home / Training / Access management
New · ISO/IEC 27001 Annex A · BSI ORP.4 · Segregation of duties
Who may do what – and why still? The course teaches how accounts and access rights are requested, approved, changed and revoked in a traceable way, and how to run a recertification that is decided on business grounds and can be evidenced. This is how business units, HR and IT work together. For IT administration, application owners, managers with approval authority, HR interfaces, ISOs and internal control owners; a basic understanding of user accounts and applications is assumed.
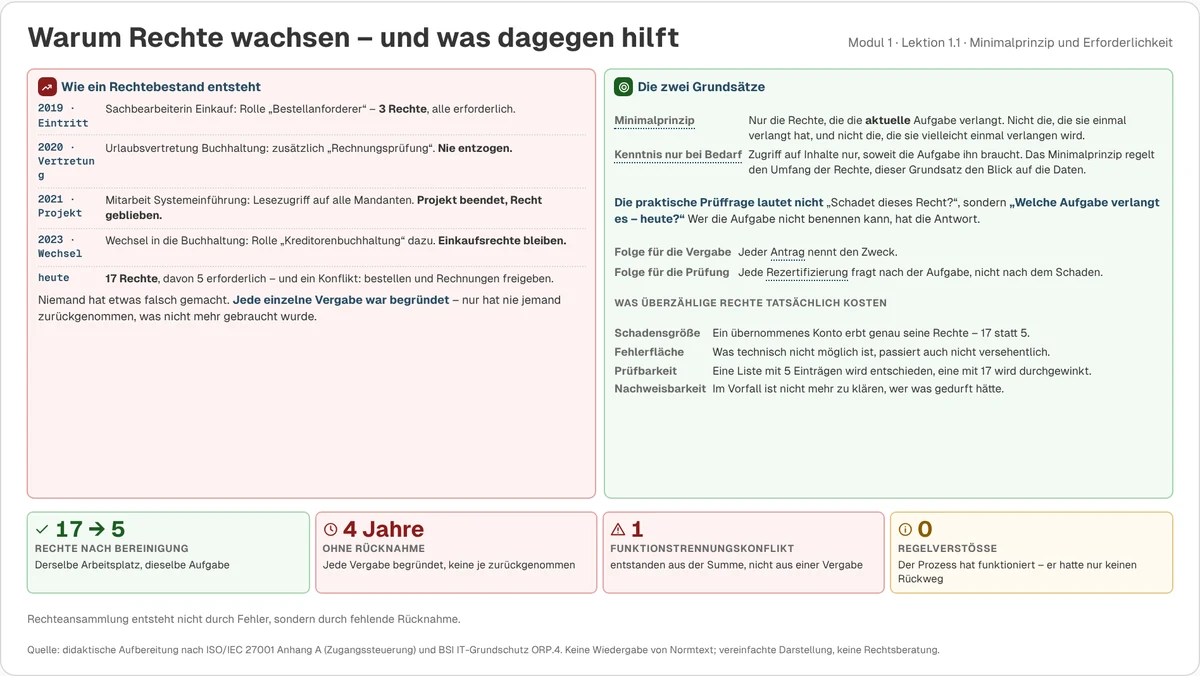
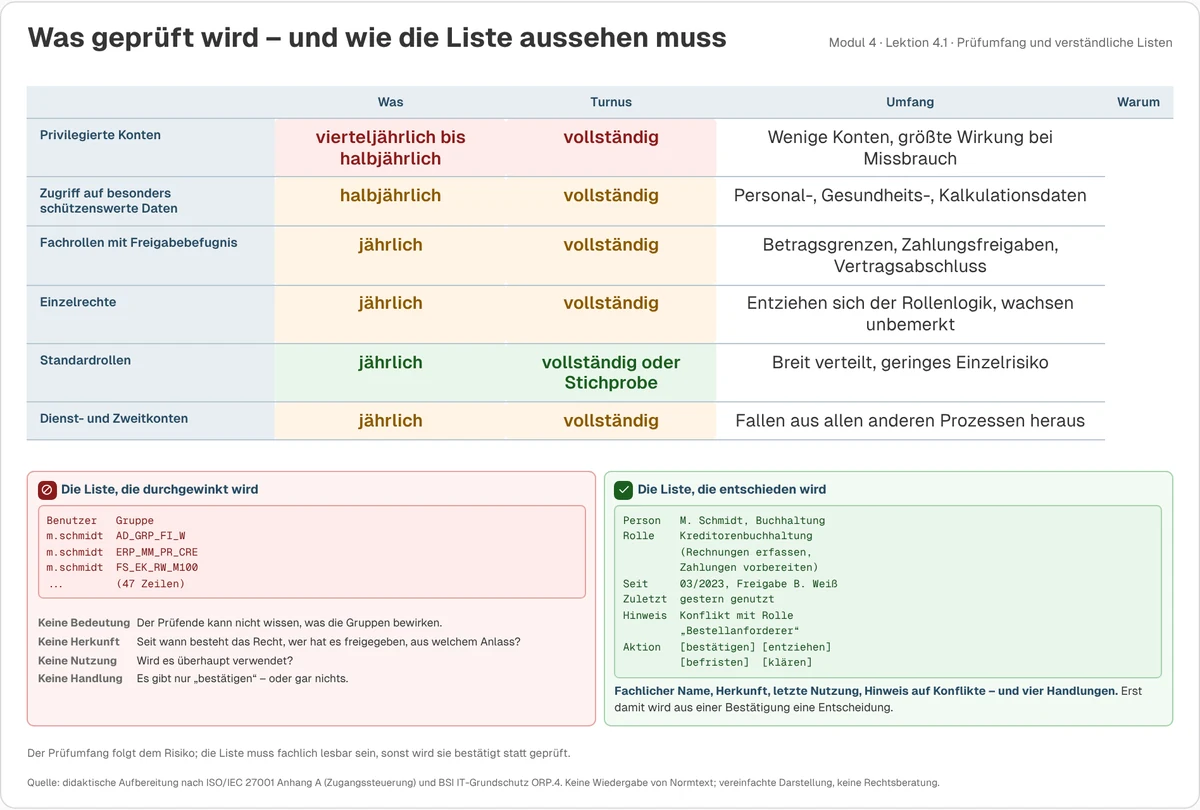
In almost every organisation, employees have more rights than they need – not through rule-breaking, but because rights are granted one by one and never taken back. On a role change old rights remain, after leaving accounts are locked instead of rights being revoked, recertification lists with technical group names are waved through, and service, emergency and external accounts fall outside every process.
ISO/IEC 27001 Annex A requires controlled access, identity management, management of privileged access rights and regular review of access rights; the BSI module ORP.4 describes the procedure. The course counters this with separate roles for request, approval, implementation and control, the role change treated as a rebuild, and lists that can be decided on business grounds.
Least privilege, need to know; who requests, approves, implements and controls
Triggering from the HR system, rebuild on role change, locking, revocation and deletion with deadlines
Role model and individual rights, privileged accounts, service accounts, externals and emergency access
Scope by risk, readable lists, four decisions, revocation and closing check
Twelve cases from a real set of access rights: decide, justify, resolve conflicts, document
Six metrics with the actions that follow from them, and a personal action plan

Access rights in practice: in Vercora you manage access rights with segregation of duties and recertification as part of the ISMS. The matching audit approach is taught in Conducting Internal ISMS Audits in Practice, whose continuous case is also an access management process.
Auditor’s view
“The question is never whether a right does harm, but which task requires it today. Whoever asks this with every request needs the other rules less often.”
Heinrich Markus Schulte · IT auditor and expert witness
Brochure as PDF (4 pages, 840 KB)
How to book: Individually without a subscription: €399 net per person, 12 months of access. As an add-on to the subscription at the same price per person. Complements the courses on internal ISMS audits, risk assessment and BSI Grundschutz++.
Live Add live: Office hour 60 min. for your questions, €290 · workshop 3 hrs, e.g. setting up an access control policy and recertification for your organisation, €890
Request a live sessionCompany-wide licence, white label and operation on your own web space on request; test access and demo on request. Basis: requirements of ISO/IEC 27001 (Annex A, access control) and BSI IT-Grundschutz module ORP.4; standard texts are not reproduced. The applicable original documents and your organisation’s access control policy, deadlines and approval rules are decisive. Legal status November 2026. The certificate confirms attendance; it is not a certification and not an audit opinion. Not legal advice. “BSI” is a trademark of the BSI.
Related
Single seat, annual subscription or training package
Together we put together a training package that fits your responsibilities and your qualification needs. All courses run on the Vercora training portal, with knowledge checks and a certificate of attendance that can be verified online.