Sec. 38(3) BSIG
NIS2 management board training
For managing directors and executive boards, aligned with the BSI curriculum.
from €249 net per person
Content and prices →Home / Training
Online compliance training · NIS2 · CRA
Three online courses for management, information security and product development. With knowledge checks, a numbered certificate of attendance and evidence documents that stand up to supervisors and auditors.
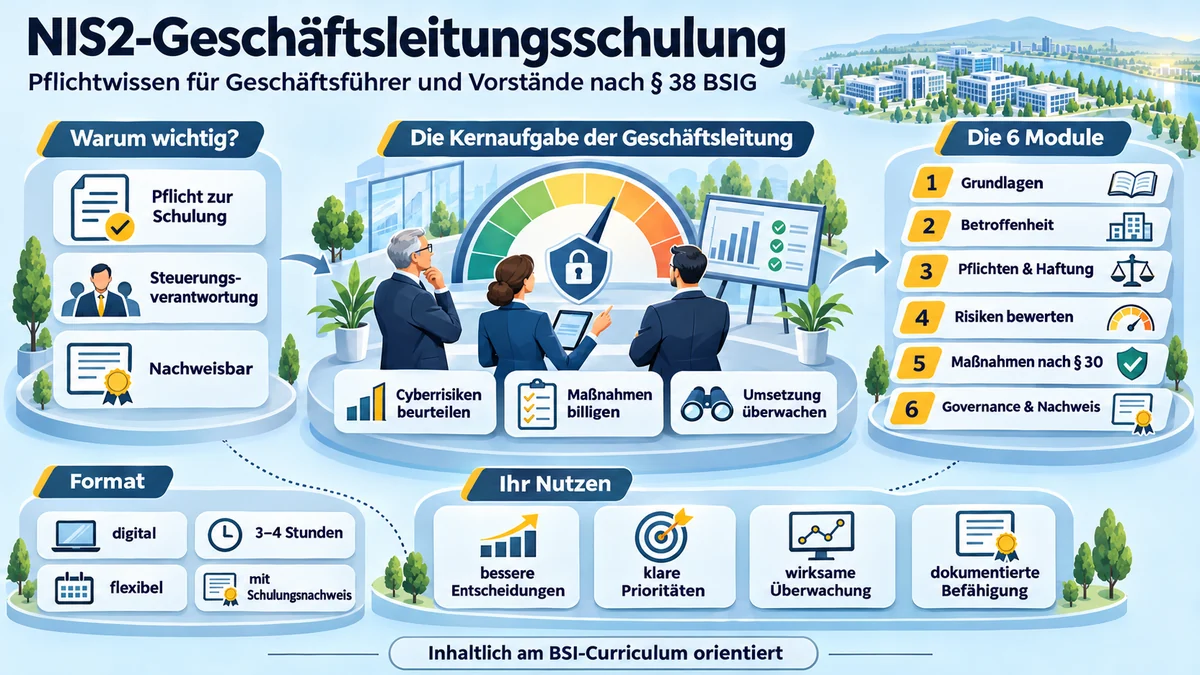
The management board training at a glance: core tasks, six modules, format and benefits.
The programme at a glance
Every course ends with a verifiable certificate. You book individual seats or a team licence for up to five people.
Sec. 38(3) BSIG
For managing directors and executive boards, aligned with the BSI curriculum.
from €249 net per person
Content and prices →Sec. 30(2) no. 7 BSIG
For those leading the annual incident response exercise.
from €149 net per person
Content and prices →Regulation (EU) 2024/2847
For product, development and security teams at manufacturers.
from €199 net per person
Content and prices →How it works
You book seats per course. Your contact person receives access to the training portal.
Each person receives a personal invitation link, without a password and usable on any device.
Lessons with knowledge checks, passed from 75%. Progress is saved.
Certificate of attendance as a PDF by email, with a number and online authenticity check.
Sec. 38(3) BSIG · aligned with the BSI curriculum
Assess cyber risks. Have measures implemented and oversee them. Provide the evidence.
Managing directors and board members of important and essential entities. Under Sec. 38(3) BSIG they must attend training regularly. The course teaches oversight competence, not technology.
Preparation on your own company (required) → six modules → certificate → follow-up with board resolutions.
Applicability, services, OT, group structures, service providers
Implement and oversee, fines, business judgement rule
Assets, protection goals, risk overview, residual risks
Ten measures in six areas, register of measures
Secs. 32–35 BSIG, 24 h / 72 h, three decision cases
Regular report, BSI audit, key questions, resolutions
Evidence: the certificate of attendance states the person, role, company, period, time spent, results, course version and the reference to Sec. 38(3) BSIG, with all lessons, results and competence mapping in the annex. Authenticity verifiable online.
€249 net per person
Recommended
€349 net per person
€1,190 net for up to 5 people
€1,790 net for up to 5 people
Prices net plus VAT. Aligned with the BSI curriculum for NIS2 management board training; not certified or approved by the BSI.
Sec. 30(2) no. 7 BSIG · Incident response exercise
The course for everyone leading the annual tabletop exercise on incident response and contingency planning: from the scenario to an audit-ready exercise record.
Information security officers, IT management and those responsible for emergency and crisis management in important and essential entities. Based on the BSIG as amended by the German NIS2 Implementation Act (NIS2UmsuCG), with Implementing Regulation (EU) 2024/2690 as a guide.
Evidence: numbered certificate of attendance with online verification as role-based training for exercise leads under Sec. 30(2) no. 7 BSIG. It does not replace management board training under Sec. 38(3) BSIG.
€149 net per person
Recommended
€590 net for up to 5 people
€990 net for up to 5 people
Prices net plus VAT. The course prepares the exercise lead; running the exercise in your company is not included and can be commissioned separately. No legal advice.
Cyber Resilience Act · Regulation (EU) 2024/2847 · BSI TR-03183-2
Create, maintain and evidence software bills of materials, plus the other manufacturer obligations up to CE marking.
Product owners, development teams and security and risk managers at manufacturers of products with digital elements. The reporting obligations under Art. 14 CRA have applied since 11 September 2026, all other obligations apply from 11 December 2027.
What an SBOM is and why the CRA requires it
Components, PURL, hashes, retention
CycloneDX and SPDX, VEX, TR-03183-2 requirements
Pipeline, monitoring, reporting under Art. 14
Roles, risk, Annex I, CE, market surveillance
Summary, next steps, final quiz
Legal basis: Regulation (EU) 2024/2847, the German implementation act (passed by the Bundestag on 15 October 2026, BSI as market surveillance authority) and BSI TR-03183-2. Evidence: verifiable certificate of attendance; it proves the training, not the conformity of a product.
€199 net per person
Recommended
€790 net for up to 5 people
€1,290 net for up to 5 people
Prices net plus VAT. The CRA has no personal training obligation; the course supports the implementation of manufacturer obligations. Based on the course “CRA SBOM Fundamentals” from open-isms (AGPL-3.0), revised and extended. No legal advice.
An auditor's view, not standard e-learning
Heinrich Markus Schulte, IT auditor and expert for information security and resilience, with more than 30 years of hands-on IT experience. The courses show not only what the law says, but which information, decisions and evidence actually count in an audit.
Frequently asked questions
Under Sec. 38(3) BSIG, the management of important and essential entities must attend training regularly so they can assess cyber risks and risk management practices. Training the IT manager or information security officer does not replace this.
No. The management board training is aligned with the BSI curriculum for NIS2 management board training. All courses are independent offerings of Sachverständigenbüro Schulte and are not certified or approved by the BSI.
Each participant receives a personal invitation link, without a password and usable on any device. Progress is saved; a knowledge check is passed from 75%. The certificate of attendance arrives as a PDF by email, with a number and online authenticity check.
No. The tabletop training is role-based training for exercise leads under Sec. 30(2) no. 7 BSIG. It does not fulfil management's training obligation under Sec. 38(3) BSIG.
The Cyber Resilience Act has no personal training obligation. The CRA course helps manufacturers implement their obligations, such as the SBOM under Annex I Part II no. 1 and the reporting obligations under Art. 14. The certificate proves the training, not the conformity of a product.
Access is valid for 12 months including updates. All three courses are available in German and English.
Request seats
Choose a course and package. You will receive a quote with an invoice; after booking, the office sets up your access to the training portal.
More than five participants or several courses? Just say so in your message.
The courses are independent offerings of Sachverständigenbüro Schulte and are not certified or approved by the BSI. No legal advice.