Assignment, roles and planning
Distinction from consulting and line control, independence, objective, scope, criteria, risk-based audit plan
Home / Training / Internal ISMS audits
New · ISO/IEC 27001 clause 9.2 · ISO 19011 · DORA
Internal audits that hold up: the course enables you to prepare, conduct and document a defined ISMS audit in a traceable way. You set audit criteria and scope, plan on a risk basis, conduct interviews and samples, assess the evidential value of evidence and formulate findings that withstand scrutiny. A continuous case, the audit of an access management process, accompanies you through to the final quiz. For internal auditors, information security officers, compliance officers, internal audit and employees with control tasks; basic knowledge of an ISMS is assumed.
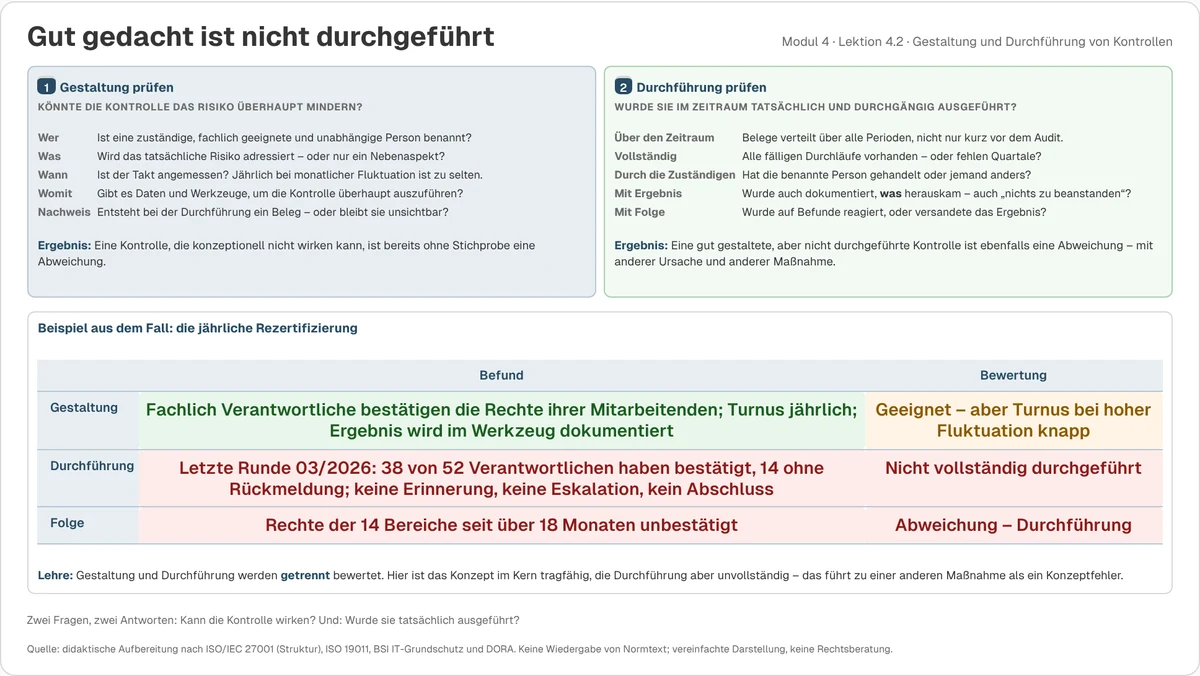
Rarely for lack of expertise, mostly because of method: a finding without a named criterion, a sample without a population, the design and operation of a control lumped together, a conclusion that claims more than the evidence supports.
Yet ISO/IEC 27001 requires internal audits at planned intervals (clause 9.2), and DORA requires the regular review of the ICT risk management framework by internal audit (Art. 6). The course counters this with a consistent methodology based on ISO 19011 and BSI IT-Grundschutz: criteria before the first audit procedure, evidence assessed against five characteristics, findings with a fixed structure.
Distinction from consulting and line control, independence, objective, scope, criteria, risk-based audit plan
Conducting interviews, reviewing documents and observing, drawing samples and knowing their limits
Evidential value, design and operation of controls, contradictions, gaps and timeliness
Structure of a robust finding, deviation, risk and cause, rating and wording
Case file, audit plan and sample, contradictory statements, evidence review, writing the finding
Audit report, measures, effectiveness review and closure
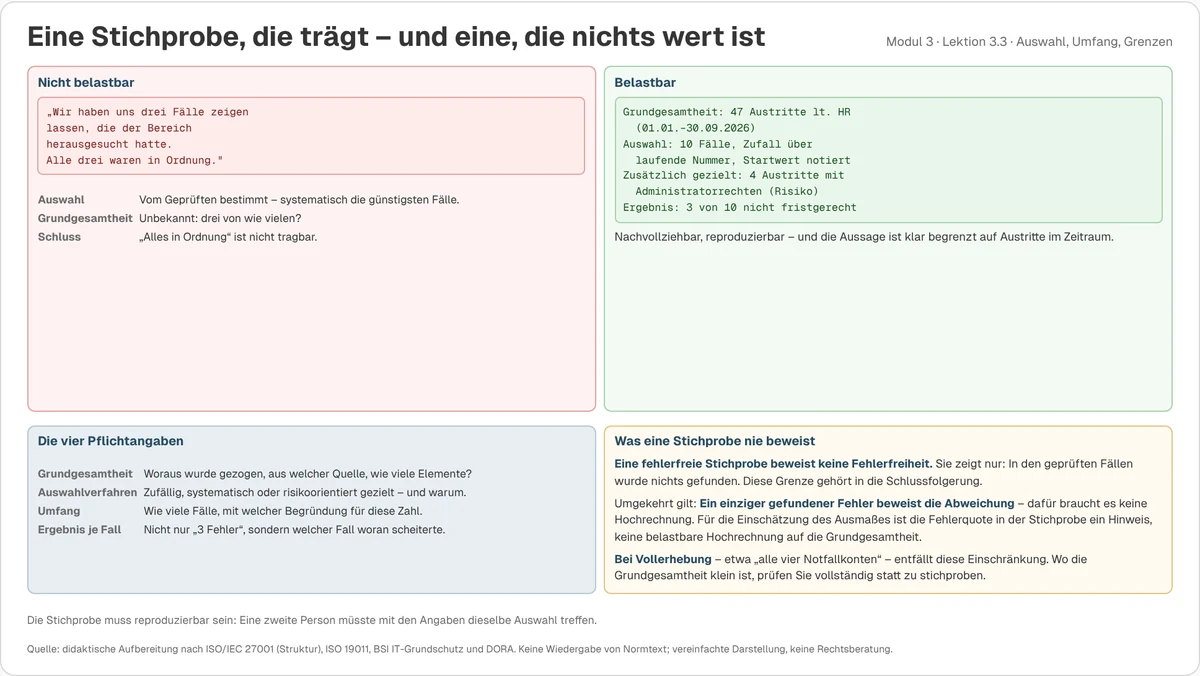
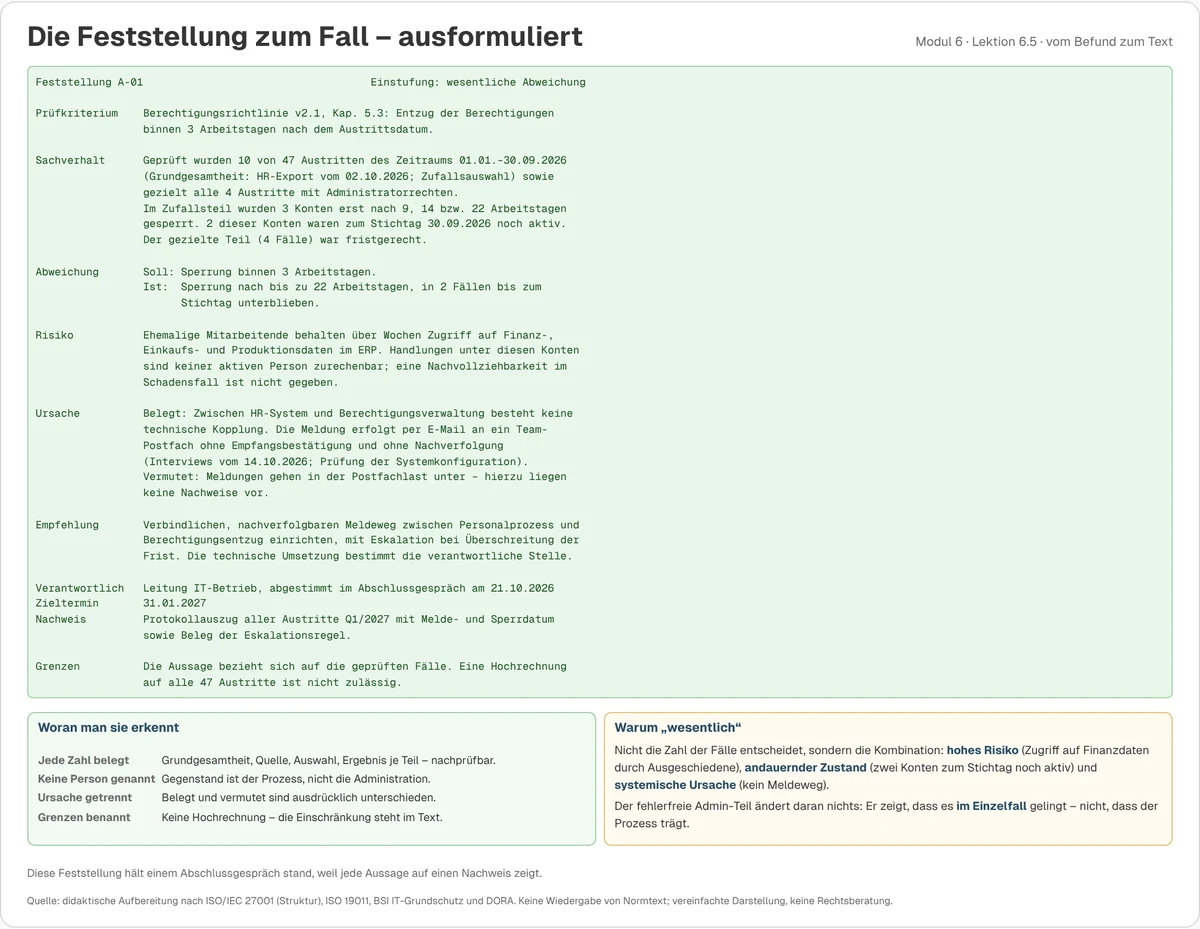
Audits in practice: in Vercora you conduct audits with question catalogues and audit programmes, including for ISO 27001 and DORA, track findings and measures and evidence their effectiveness. If you need audits by an independent third party: IT audit by the expert office.
Auditor’s view
“An audit is worth as much as the evidence it rests on. This course teaches exactly the craft that turns an impression into a robust finding.”
Heinrich Markus Schulte · IT auditor and expert witness
Brochure as PDF (4 pages, 880 KB)
How to book: Individually without a subscription: €399 net per person, 12 months of access. As an add-on to the subscription at the same price per person. Complements the courses on BSI Grundschutz++, DORA and outsourcing management.
Live Add live: Office hour 60 min. for your questions, €290 · workshop 3 hrs, e.g. setting up an audit programme and audit plan for your ISMS, €890
Request a live sessionCompany-wide licence, white label and operation on your own web space on request; test access and demo on request. Basis: structure of ISO/IEC 27001 (clause 9.2 and Annex A), ISO 19011 guideline, BSI IT-Grundschutz and the DORA requirements for internal audit; standard texts are not reproduced. Legal status November 2026. The certificate confirms attendance; it is not an auditor certification and not an audit opinion. Not legal advice. “BSI” is a trademark of the BSI.
Related
Single seat, annual subscription or training package
Together we put together a training package that fits your responsibilities and your qualification needs. All courses run on the Vercora training portal, with knowledge checks and a certificate of attendance that can be verified online.