Member of BISG e. V. · Düsseldorf +49 151 12479963sachverstaendiger@itschulte.deVercora login

Home / Training / CRA: SBOM and manufacturer obligations

Cyber Resilience Act · Regulation (EU) 2024/2847 · BSI TR-03183-2

CRA: SBOM and manufacturer obligations

Create, maintain and evidence software bills of materials, plus the other manufacturer obligations up to CE marking.

Scope
6 modules
Lessons
14
Knowledge checks
63 questions
Duration
approx. 100 min.
Pass mark
from 75%

Who it is for

Product owners, development teams and security and risk managers at manufacturers of products with digital elements. The reporting obligations under Art. 14 CRA have applied since 11 September 2026, all other obligations apply from 11 December 2027.

Your benefits

  • Implement the SBOM requirement under Annex I Part II no. 1
  • Understand tools such as cdxgen, Syft, Grype and Dependency-Track
  • Reporting chain: 24 h early warning, 72 h notification, final report
  • Know the conformity route for each product class
Module 0

Fundamentals

What an SBOM is and why the CRA requires it

Module 1

What belongs in an SBOM

Components, PURL, hashes, retention

Module 2

Formats

CycloneDX and SPDX, VEX, TR-03183-2 requirements

Module 3

Create and maintain

Pipeline, monitoring, reporting under Art. 14

Module 4

Other manufacturer obligations

Roles, risk, Annex I, CE, market surveillance

Module 5

Wrap-up

Summary, next steps, final quiz

Legal basis: Regulation (EU) 2024/2847, the German implementation act (passed by the Bundestag on 15 October 2026, BSI as market surveillance authority) and BSI TR-03183-2. Evidence: verifiable certificate of attendance; it proves the training, not the conformity of a product.
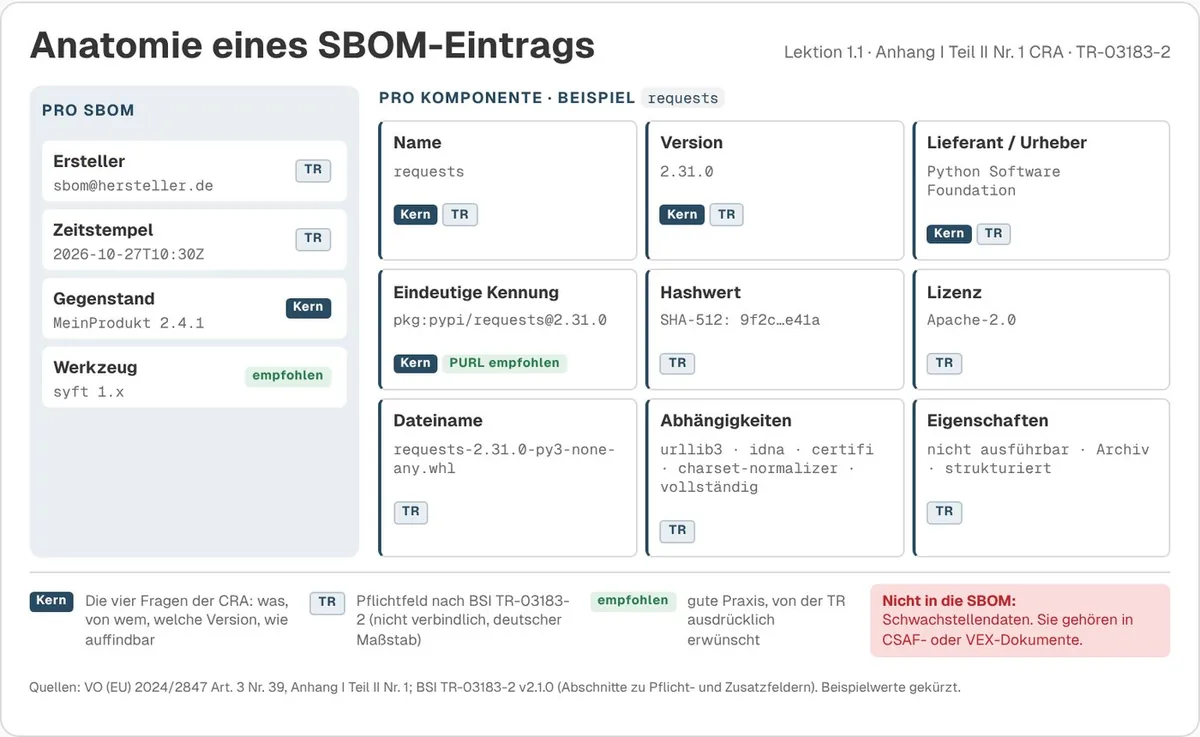
Anatomy of an SBOM entry: details per SBOM such as author, timestamp and tool, and per component name, version, supplier, unique identifier (PURL), hash, licence and dependencies, marked by CRA core and BSI TR-03183-2
Anatomy of an SBOM entry. Mandatory fields under the CRA and TR-03183-2.
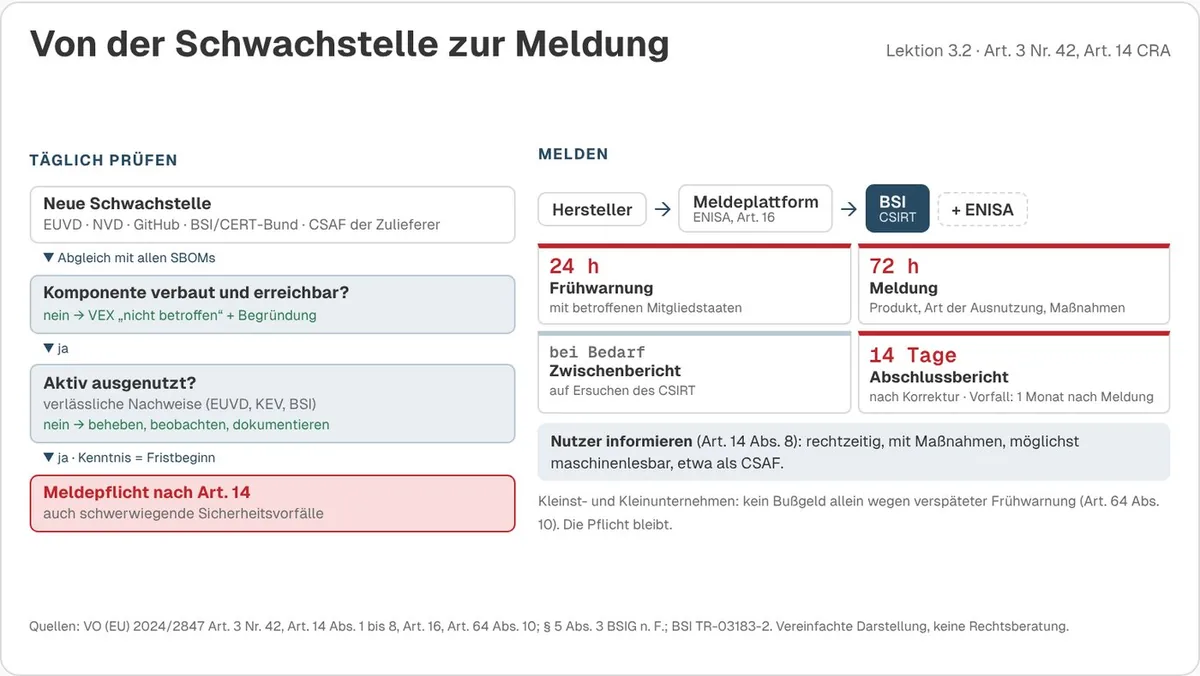
Process from a new vulnerability to reporting under Art. 14 CRA: daily matching against all SBOMs, check for active exploitation, early warning within 24 hours, notification within 72 hours and final report after 14 days via the reporting platform
From vulnerability to report. Deadlines and channels under Art. 14 CRA.
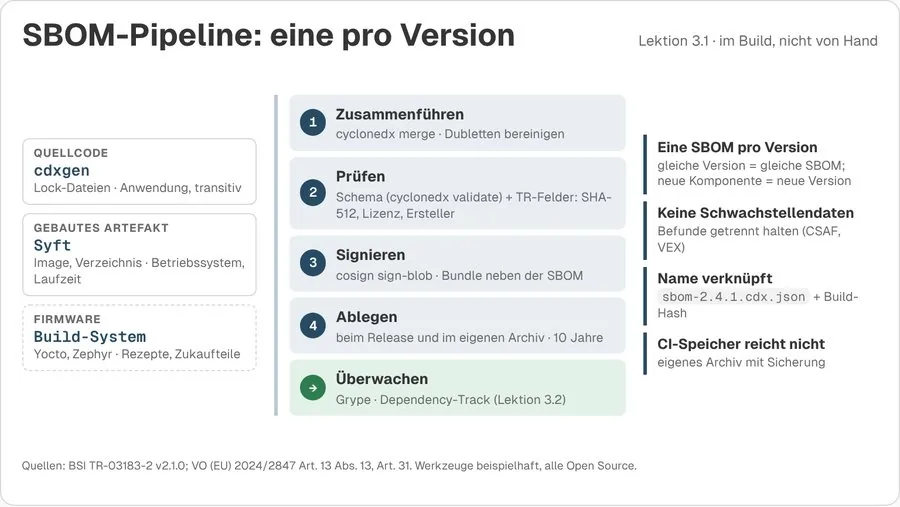
SBOM pipeline with one SBOM per version: generate from source code, built artefact and firmware, merge, validate, sign, archive and monitor for vulnerabilities
SBOM pipeline. One SBOM per version, generated in the build.
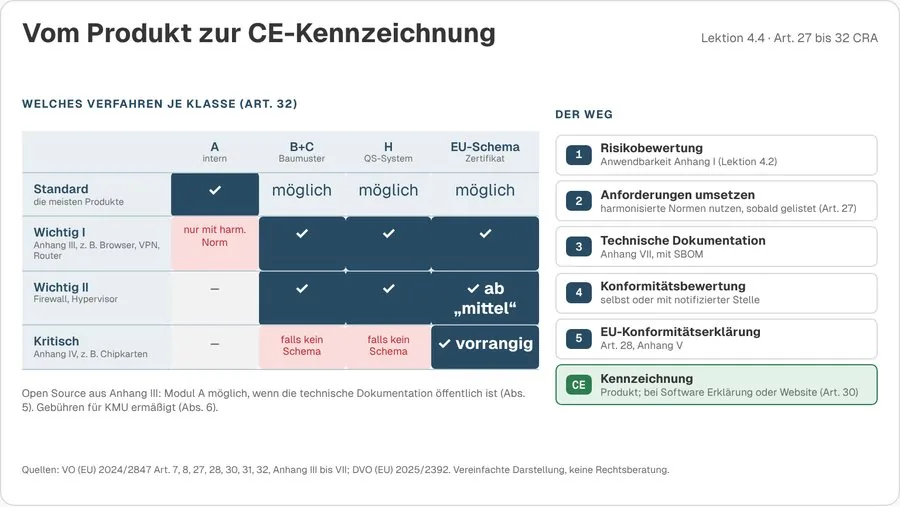
Table of conformity assessment procedures per product class under Art. 32 CRA and the path from risk assessment via technical documentation and EU declaration of conformity to CE marking
From product to CE marking. Procedures per product class.
Heinrich Markus Schulte

Auditor’s view

“In audits the SBOM is not read but tested: is it complete, up to date and linked to the vulnerability process?”

Heinrich Markus Schulte · IT auditor and expert witness

Questions supervisors and auditors ask

  • Is there an SBOM for every version shipped?
  • How quickly can you tell whether a new vulnerability affects your products?
  • Who reports an actively exploited vulnerability within 24 hours?
  • Which conformity route applies to your product?

Brochure as PDF (4 pages, German, 760 KB)

How to book: As an add-on to the subscription for €690 net per year (up to 5 people). Single seat without subscription: €199 net per person, 12 months of access.

Live Add live: Office hour 60 min. for your questions, €290 · Workshop 3 hrs, e.g. set up the SBOM process for your product, €890

Request a live session

The CRA has no personal training obligation; the course supports the implementation of manufacturer obligations. Based on the course “CRA SBOM Fundamentals” from open-isms (AGPL-3.0), edited and extended. Not legal advice.

Related

More courses for these responsibilities

All 25 courses at a glance → Find courses by target group

Single seat, annual subscription or training package

Talk to us

Together we put together a training package that fits your responsibilities and your qualification needs. All courses run on the Vercora training portal, with knowledge checks and a certificate of attendance that can be verified online.