Protection needs and network overview
Protection needs per system, data flows per business process, seven recurring trust boundaries
Home / Training / Network security
New · ISO/IEC 27001 Annex A · BSI NET.1.1, NET.1.2, NET.3.2, NET.2.1, OPS.1.2.5 and DER.1
A device is compromised. From then on, the network decides. The course shows how to identify protection needs and data flows, separate the network into zones, control communication, secure remote access and administration, monitor, and contain an incident in a prepared way. For network, system and cloud administration, those responsible for firewalls and remote access, application support with network relevance and CISOs as well as IT operations management and those responsible for service provider management, IT budget and investment.
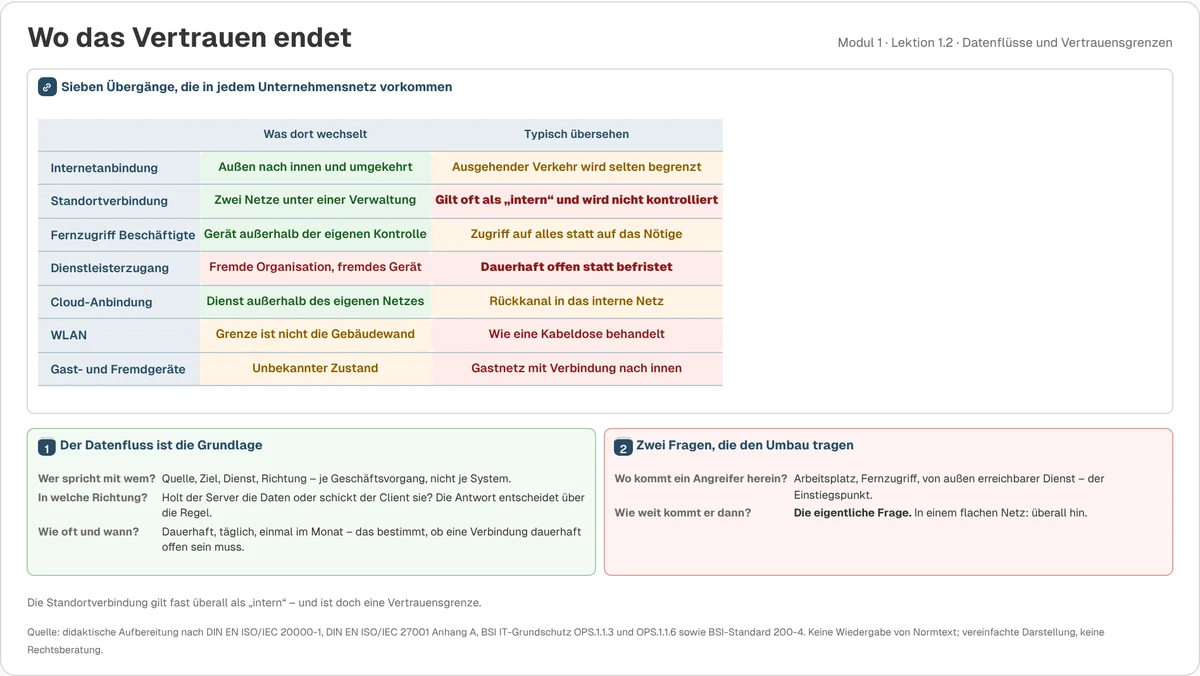
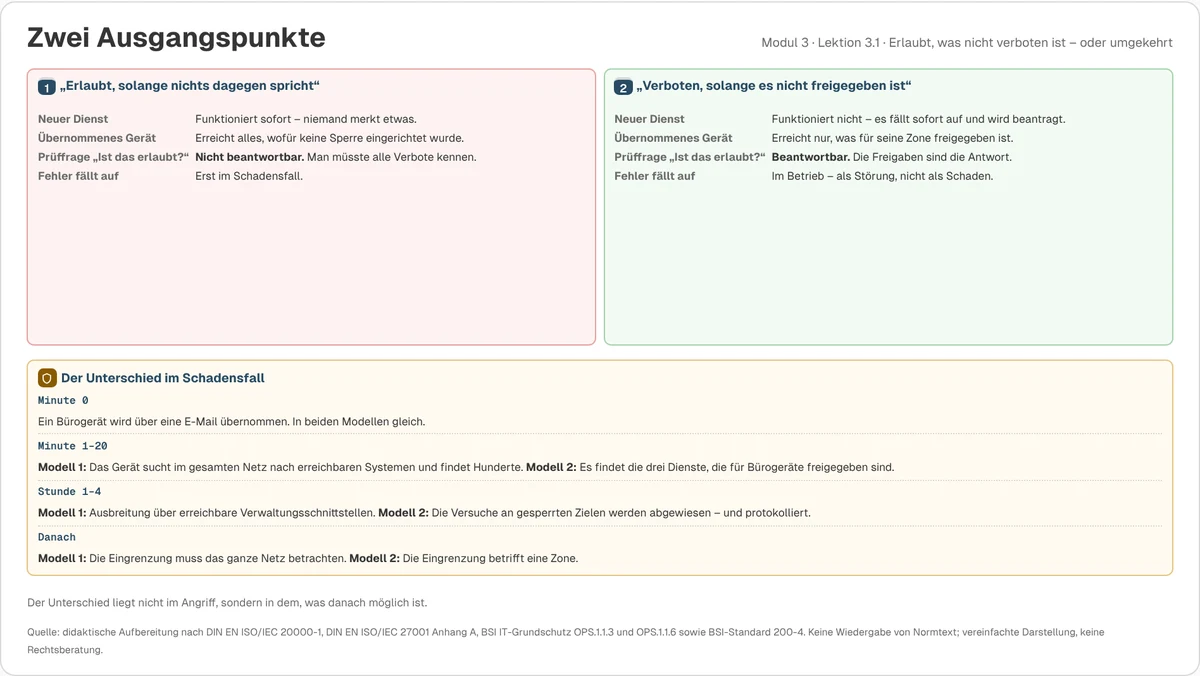
Network security does not prevent the break-in. It decides what is possible afterwards: whether a compromised office device reaches hundreds of systems or the three services in its zone. A flat network is not the result of a decision but of no decision ever being made. Separation fails because nobody knows which connections are needed, the rule set grows without taking effect, and access outlives the contracts it was set up for.
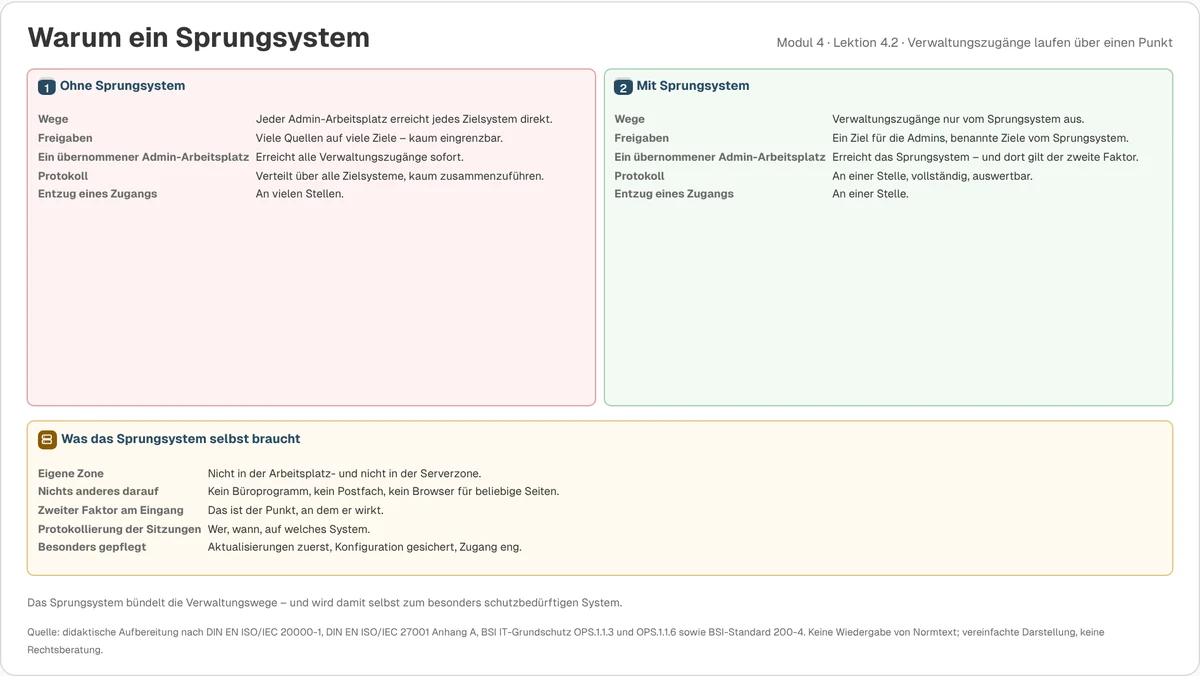
The course counters this with protection needs per system instead of “everything is critical”, data flows per business process, zones of equal protection needs, a default deny with justified exceptions, a jump host for administrative access, four ways in from outside with four treatments, rejected connections as the most important log source and three prepared containment levels with named authority. It deliberately does not give vendor-specific configurations; OT is only delimited.
Protection needs per system, data flows per business process, seven recurring trust boundaries
Rebuild in four steps, Wi-Fi and guests, cloud, sites and the OT boundary
Default deny, rule request and justification, shadowed rules, rule maintenance and review
Four groups and four routes, jump host, separate accounts, service provider access
Hardening and default accounts, updates, configuration backup, redundancy, central services
What is recorded, suspicious communication, three prepared containment levels
Network plan, communication list, rule extract, zone design, access routes and action plan
Responsibilities, recurring reviews, exceptions and transfer
Network security in context: who receives which rights and gives them up again is covered in Access management; which gap is closed first, in Vulnerability management. If containment turns into an incident, this is handled by Incident Response and Playbooks.
Auditor’s view
“Network security does not prevent the break-in. It decides whether it becomes an incident or a disaster.”
Heinrich Markus Schulte · IT auditor and expert witness
Brochure as PDF (4 pages, 660 KB)
How to book: Individually without a subscription: €399 net per person, 12 months’ access. As an add-on to the subscription at the same price per person. Complements the courses on access management, vulnerability management and incident response.
Live Add live: Consultation hour 60 min. for your questions, €290 · Workshop 3 hrs, e.g. defining the zone model, rule request and containment levels for your network, €890
Request a live sessionCompany-wide licence, white label and operation on your own web space on request; test access and demo on request. Basis: DIN EN ISO/IEC 27001 (Annex A: network security, network services, segregation of networks, access control, logging) and BSI IT-Grundschutz modules NET.1.1, NET.1.2, NET.3.2, NET.2.1, OPS.1.2.5 and DER.1; standard texts are not reproduced. Vendor-specific configurations and universal rule sets are deliberately not taught, OT is only named as a boundary; your organisation’s protection needs and requirements are authoritative. Legal status November 2026. The certificate confirms attendance; it is not a certification or audit opinion. No legal advice. “BSI” is a mark of the BSI.
Related
Single seat, annual subscription or training package
Together we put together a training package that fits your responsibilities and your qualification needs. All courses run on the Vercora training portal, with knowledge checks and a certificate of attendance that can be verified online.