Basics and roles
Purpose, scope, three change classes; roles and approval limits
Home / Training / Change management
New · ISO/IEC 20000-1 · ISO/IEC 27001 Annex A · BSI OPS.1.1.3 and OPS.1.1.6 · BSI 200-4
Most disruptions begin as an approved change. The course shows how to request changes completely, find dependencies, approve them according to risk, carry them out with a way back and close them verifiably. For system, network and application administration, application support, change managers and technical service providers as well as IT management, team leads, owners of business-critical services and managers with approval and escalation responsibility.
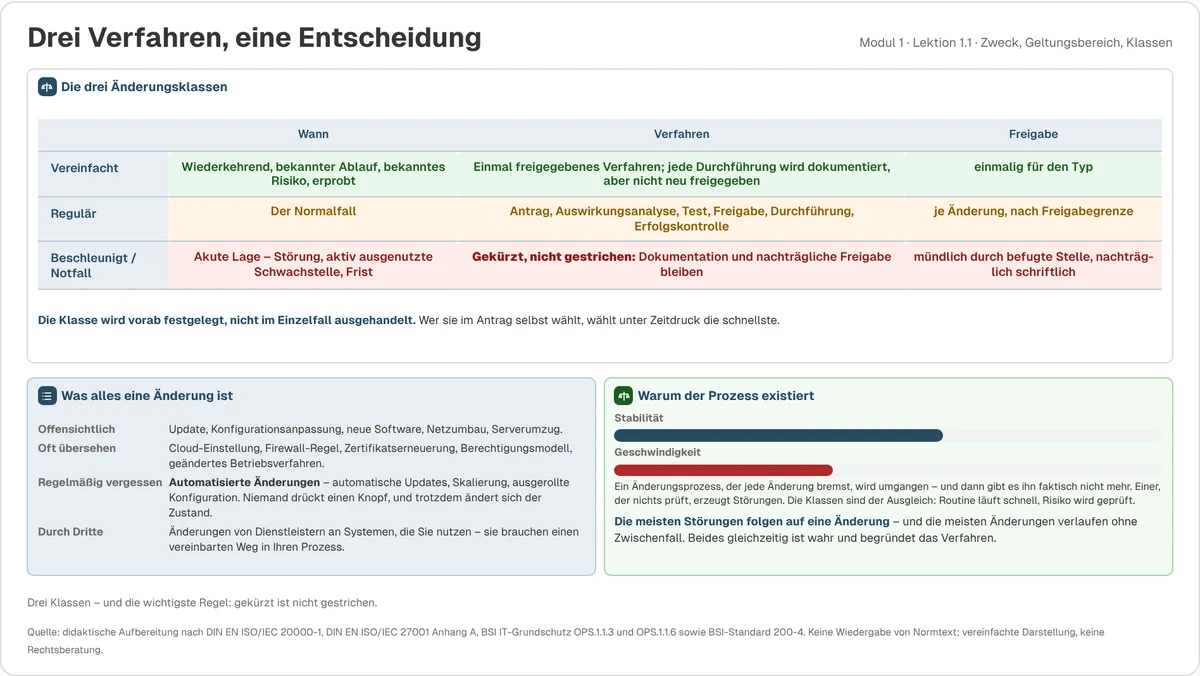
It is not the complicated change that is dangerous, but the one nobody considered dangerous: an update that quietly switches an exchange format, a maintenance window with no time for rollback, an approval nobody read. The “out of scope” field stays empty, and the emergency route becomes the standard route until nobody can tell which change was really urgent.
The course counters this with a request with twelve details, six directions of dependency analysis, approval limits that are set before the first conflict of objectives, windows that cover execution, verification, decision and rollback, abort criteria that are not negotiated, and an emergency route that shortens without skipping steps.
Purpose, scope, three change classes; roles and approval limits
Twelve details, six directions of dependency analysis, risk instead of complexity
Test levels and success criteria, windows and conflicts, risk-based approval
Runbook with checkpoints, abort criteria, rollback, recovery, emergency changes
One change from an incomplete request to an actively exploited vulnerability
Success check, post-implementation review, five metrics, transfer to your own organisation
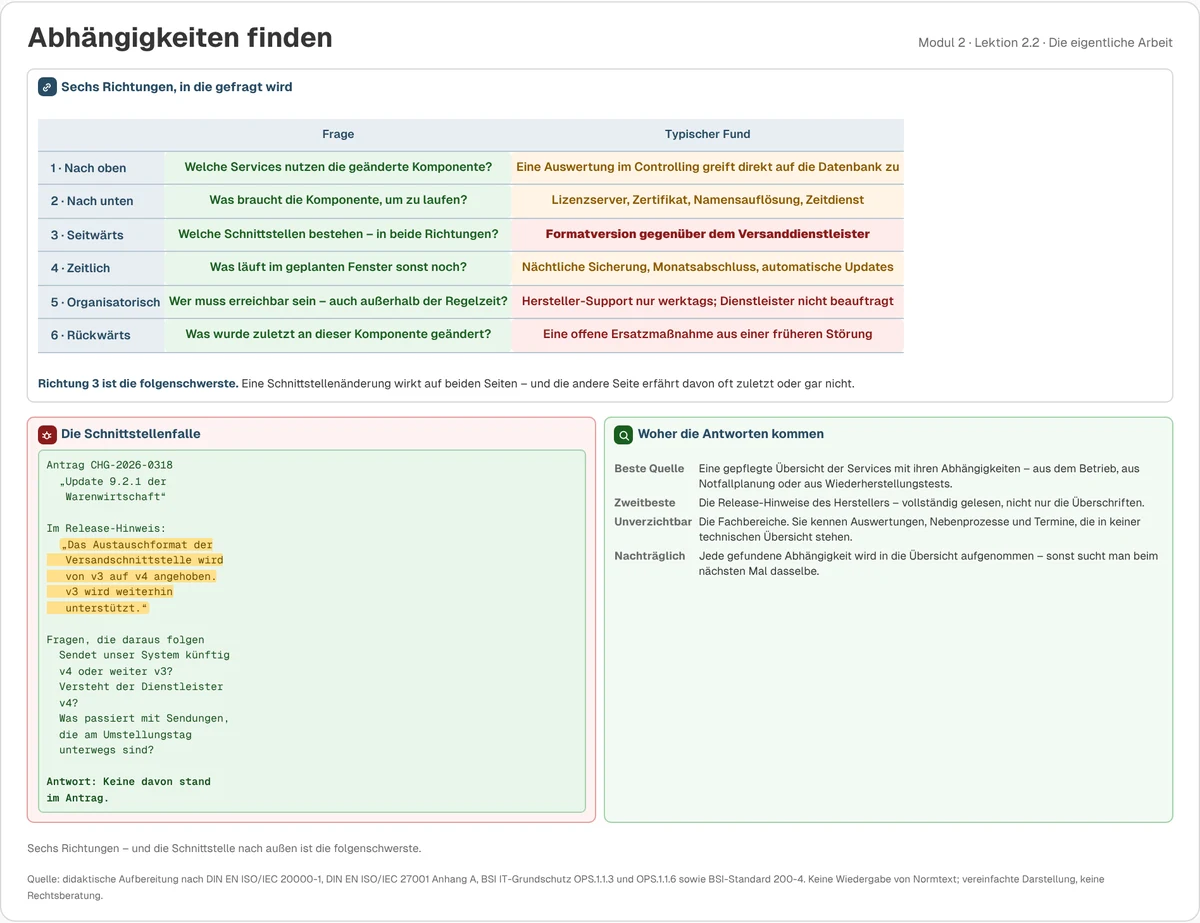
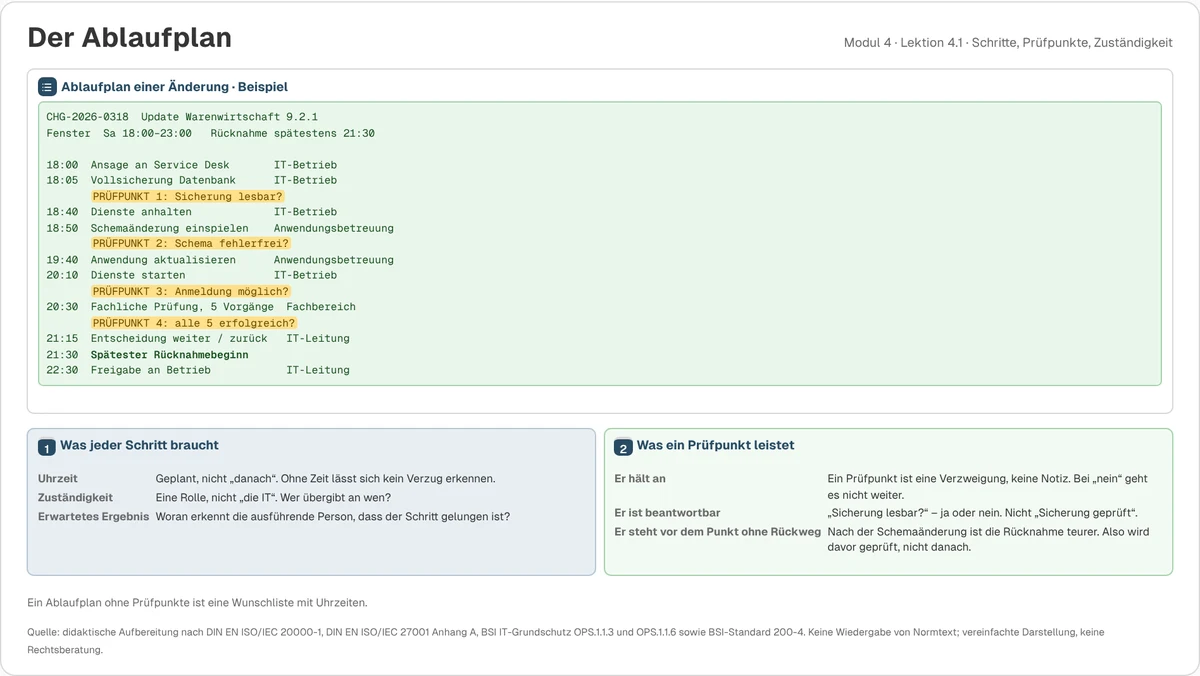
Changes in practice: in Vercora you manage changes with approval and post-implementation review, and releases with a change advisory board. If a change turns into a disruption, this is handled by Incident Response and Playbooks; whether the way back really works is shown by Restore tests.
Auditor’s view
“It is not the complicated change that is dangerous, but the one nobody considered dangerous.”
Heinrich Markus Schulte · IT auditor and expert witness
Brochure as PDF (4 pages, 790 KB)
How to book: Individually without a subscription: €399 net per person, 12 months’ access. As an add-on to the subscription at the same price per person. Complements the courses on vulnerability management, incident response and restore tests.
Live Add live: Consultation hour 60 min. for your questions, €290 · Workshop 3 hrs, e.g. defining change classes, approval limits and the emergency route for your organisation, €890
Request a live sessionCompany-wide licence, white label and operation on your own web space on request; test access and demo on request. Basis: DIN EN ISO/IEC 20000-1 (change management), DIN EN ISO/IEC 27001 (Annex A), BSI IT-Grundschutz modules OPS.1.1.3 and OPS.1.1.6 and, for the interface with emergency management, BSI Standard 200-4; standard texts are not reproduced. The valid original documents and your organisation’s change classes, approval limits and freeze periods are authoritative. Legal status November 2026. The certificate confirms attendance; it is not a certification or audit opinion. No legal advice. “BSI” is a mark of the BSI.
Related
Single seat, annual subscription or training package
Together we put together a training package that fits your responsibilities and your qualification needs. All courses run on the Vercora training portal, with knowledge checks and a certificate of attendance that can be verified online.